Identity and access management sits behind almost every digital interaction.
Employees use identity systems to access business applications. Customers use them to sign in to websites and mobile apps. Partners, suppliers, and other external users may need access to business applications and resources.
While these scenarios share the same fundamental need—securely establishing identity and controlling access—the requirements are different.
IAM primarily manages workforce identities (also known as internal identities) and access to organizational resources. CIAM is designed for external identities and customer-facing digital experiences.
The difference goes beyond who logs in. It affects authentication, user experience, identity lifecycle management, scalability, privacy, integrations, and the way organizations measure success.
In this guide, we'll compare CIAM and IAM, explain the key differences, look at their architectures and use cases, and help you determine when you need one—or both.
CIAM vs IAM: At a Glance
| Category | IAM | CIAM |
|---|---|---|
| Primary users | Employees and workforce users | Customers, consumers, members, subscribers, and other external users who do not belong to the organization. |
| Primary objective | Secure and govern access to organizational resources | Secure external identities while delivering seamless digital experiences |
| Typical applications | HR systems, productivity tools, internal applications | Websites, mobile apps, customer portals, digital products |
| Identity lifecycle | Provisioning, role changes, and offboarding | Registration, authentication, profile management, and account recovery |
| Authentication | SSO, MFA, directory-based authentication, federation | SSO, MFA, social login, passwordless, passkeys, adaptive authentication |
| User experience | Security and productivity focused | Security and customer experience focused |
| Scale | Limited by workforce population | Potentially millions of external identities |
| Privacy requirements | Workforce security and access governance | Customer data, consent, preferences, and privacy |
| Identity data | Employee attributes and organizational roles | Customer profiles, preferences, consent, and other identity attributes |
| Integrations | HR systems, directories, enterprise applications | Websites, mobile apps, APIs, CRM, commerce, marketing, and analytics platforms |
| Success metrics | Security, compliance, productivity, access governance | Conversion, engagement, security, retention, and customer experience |
The distinction is simple:
IAM secures access within an organization. CIAM secures and manages the identities of people outside the organization who interact with its digital products and services.
What Is IAM?
Identity and Access Management (IAM) refers to the security and disciplines for managing digital identities. It regulates the responsibilities and access framework privileges associated with organizational individuals and the conditions in which such privileges are allowed or denied.
IAM is most commonly associated with workforce identity. It helps organizations determine:
-
Who a user is
-
Which applications they can access
-
What they are authorized to do
-
When their access should change or be revoked
-
How access should be monitored and governed
Typical IAM capabilities include:
-
Single Sign-On (SSO)
-
Multi-Factor Authentication (MFA)
-
Role-Based Access Control (RBAC)
-
User provisioning and deprovisioning
-
Directory integration
-
Access governance
-
Privileged access controls
-
Audit and compliance reporting
What Is CIAM?
Customer Identity and Access Management (CIAM) is a specialized approach to identity management designed for customers and other external users.
These users can include:
-
Customers
-
Consumers
-
Subscribers
-
Members
-
Application users
-
Citizens
Traditional IAM is primarily concerned with securing organizational resources. CIAM has an additional challenge: The identity experience is part of the product experience.
A customer encounters identity when they register, sign in, recover an account, update their profile, authenticate on another device, or complete a sensitive transaction.
A CIAM platform therefore needs to balance security, privacy, scalability, and user experience.
Typical CIAM capabilities include:
-
Customer registration
-
Social login
-
Passwordless authentication
-
Passkeys
-
MFA
-
Adaptive or risk-based authentication
-
Progressive profiling
-
Profile and preference management
-
Consent management
-
Customer self-service
-
Fraud and bot protection
-
Identity APIs and SDKs
The 7 Key Differences Between CIAM and IAM
1. Target Audience
The most fundamental difference is who the identity system is designed to serve.
IAM primarily manages workforce identities and their access to organizational resources.
CIAM manages identities belonging to customers and other external users interacting with digital products and services.
IAM example: An employee signs in to Salesforce, Microsoft Teams, or an internal application using their corporate identity.
CIAM example: A customer creates an account on an e-commerce website, signs in with a passkey, and accesses their orders, preferences, and account information.
The authentication technology may overlap, but the surrounding requirements are different.
2. User Experience
For workforce IAM, authentication is primarily an access-control mechanism.
For CIAM, authentication is also part of the customer journey.
A customer may encounter identity during:
Registration → Login → MFA → Profile → Preferences → Purchase → Support
Every additional step can introduce friction.
That is why CIAM platforms commonly support authentication options such as:
-
Social login
-
Passwordless authentication
-
Passkeys
-
Magic links
-
Adaptive authentication
-
Flexible account recovery
The goal is to apply the appropriate level of security without creating unnecessary friction.
3. Scale and Availability
Workforce IAM typically serves a defined population of employees and other workforce users.
A customer-facing application can have a much larger and less predictable population.
A business might have:
-
20,000 employees
-
20 million customers
Those two identity populations have very different operational requirements.
CIAM platforms may need to handle:
-
Millions of identities
-
Global traffic
-
Sudden traffic spikes
-
Product launches
-
Seasonal shopping events
-
24/7 availability
-
Large authentication bursts
Scale isn't simply a matter of storing more users. It also affects authentication throughput, latency, availability, identity data, and downstream integrations.
4. Authentication and Access Methods
IAM and CIAM can use many of the same standards and security controls.
Both may support:
-
SSO
-
MFA
-
SAML
-
OAuth 2.0
-
OpenID Connect
The difference is often in how those capabilities are used.
Workforce IAM commonly integrates with enterprise directories and standardized corporate authentication.
CIAM needs to accommodate a broader range of customer journeys and authentication preferences.
Common CIAM options include:
-
Social login
-
Passwordless authentication
-
Passkeys
-
Magic links
-
SMS or email OTP
-
Biometrics
-
Adaptive authentication
-
Risk-based step-up authentication
The objective is to give customers convenient ways to authenticate while maintaining appropriate security controls.
5. Privacy and Consent
CIAM frequently handles large amounts of personal customer information.
That makes privacy an integral part of the identity architecture.
A CIAM platform may need to manage:
-
Consent
-
Communication preferences
-
Profile information
-
Data collection preferences
-
Privacy requests
-
Customer self-service
-
Regional privacy requirements
For example, a customer may need to update their communication preferences or control how their information is used without contacting customer support.
This makes CIAM more than an authentication layer. It can become an important part of the organization's customer data and privacy architecture.
6. Identity Data and Profile Management
Workforce identities tend to contain organizational attributes such as:
-
Employee ID
-
Department
-
Job title
-
Manager
-
Location
-
Role
Customer identities can be much more dynamic.
Depending on the business, customer profiles may include:
-
Contact information
-
Preferences
-
Consent
-
Loyalty information
-
Account attributes
-
Product relationships
-
Behavioral attributes
CIAM therefore needs to support more than authentication.
It needs to provide a reliable identity layer that can connect the same customer across different digital touchpoints.
For example:
Website → Mobile App → E-commerce → Customer Support → Loyalty Program
A unified identity can help maintain continuity across those experiences.
LoginRadius' CIAM architecture similarly emphasizes a centralized identity store, profile management, consent, authentication, authorization, and risk intelligence.
7. Business Objectives
IAM and CIAM ultimately support different business objectives.
IAM typically asks:
How do we securely give our workforce access to the resources they need?
IAM success can be measured through:
-
Reduced security risk
-
Faster provisioning
-
Access governance
-
Compliance
-
Improved workforce productivity
CIAM asks a broader question:
How do we securely give external users access while making the digital experience easy to use?
CIAM success can include:
-
Registration conversion
-
Login success
-
Reduced authentication friction
-
Reduced account takeover and fraud
-
Customer engagement
-
Retention
-
Reduced support volume
This is one of the biggest conceptual differences between the two.
IAM is primarily an organizational access problem. CIAM is both an identity problem and a digital experience problem.
CIAM Architecture vs IAM Architecture
The difference becomes clearer when you look at the architecture.
Typical IAM Architecture
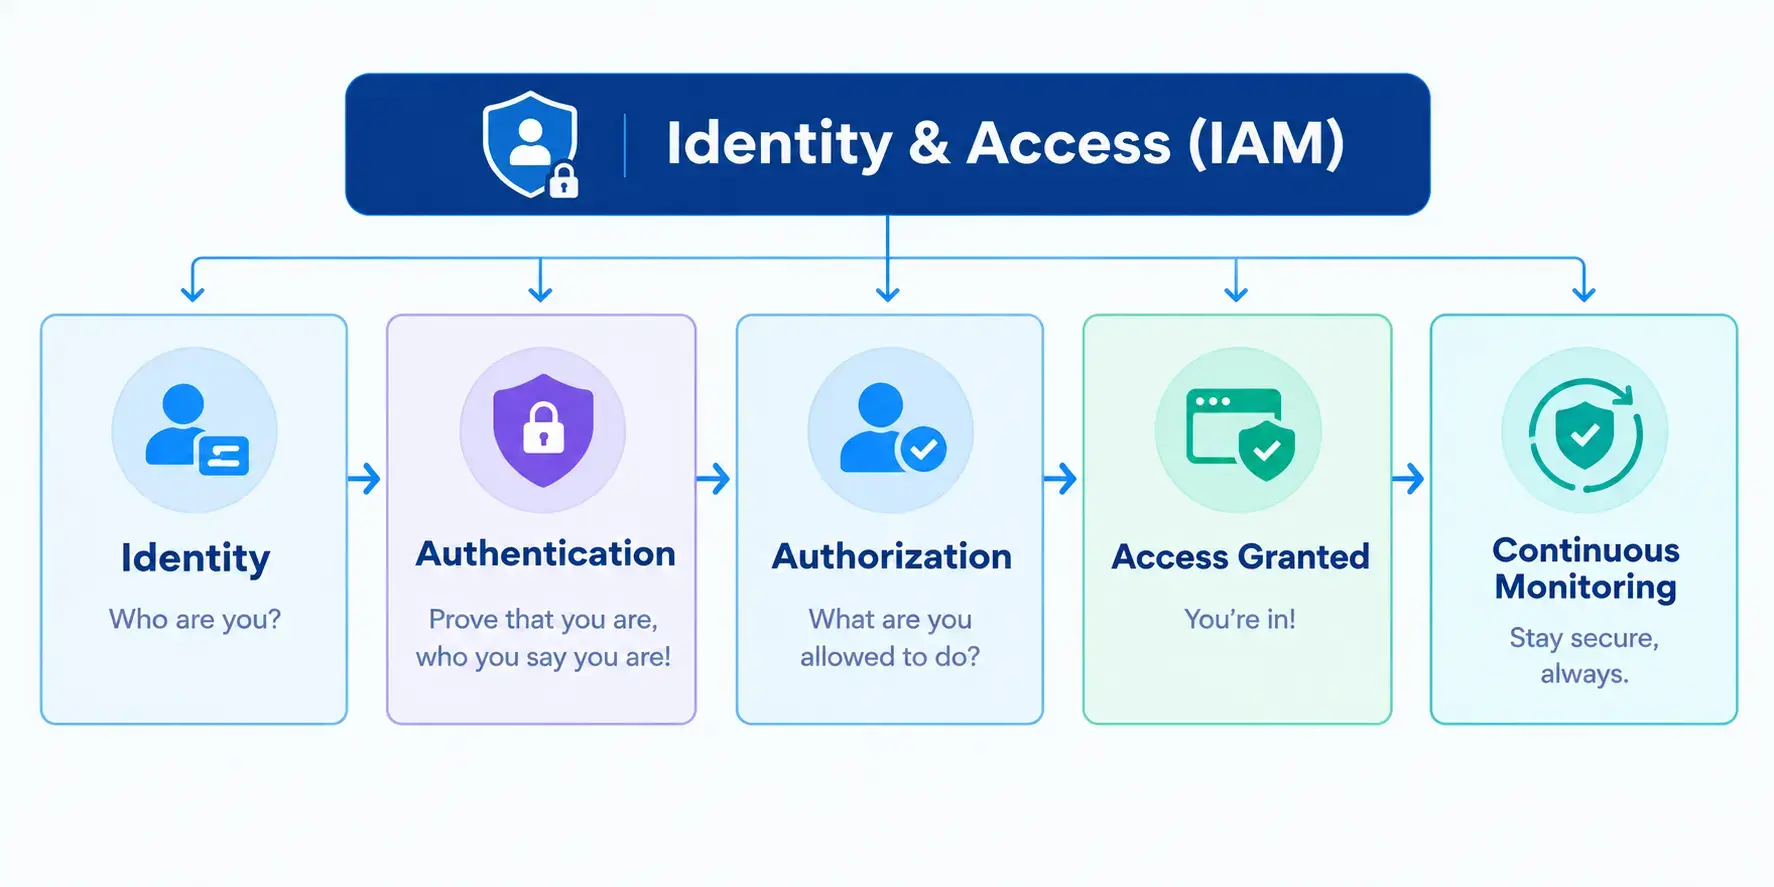
The architecture typically emphasizes:
-
Authentication
-
Authorization
-
Directory integration
-
Role and group management
-
Provisioning
-
Governance
-
Auditing
The identity is generally anchored to the organization's workforce directory.
Typical CIAM Architecture
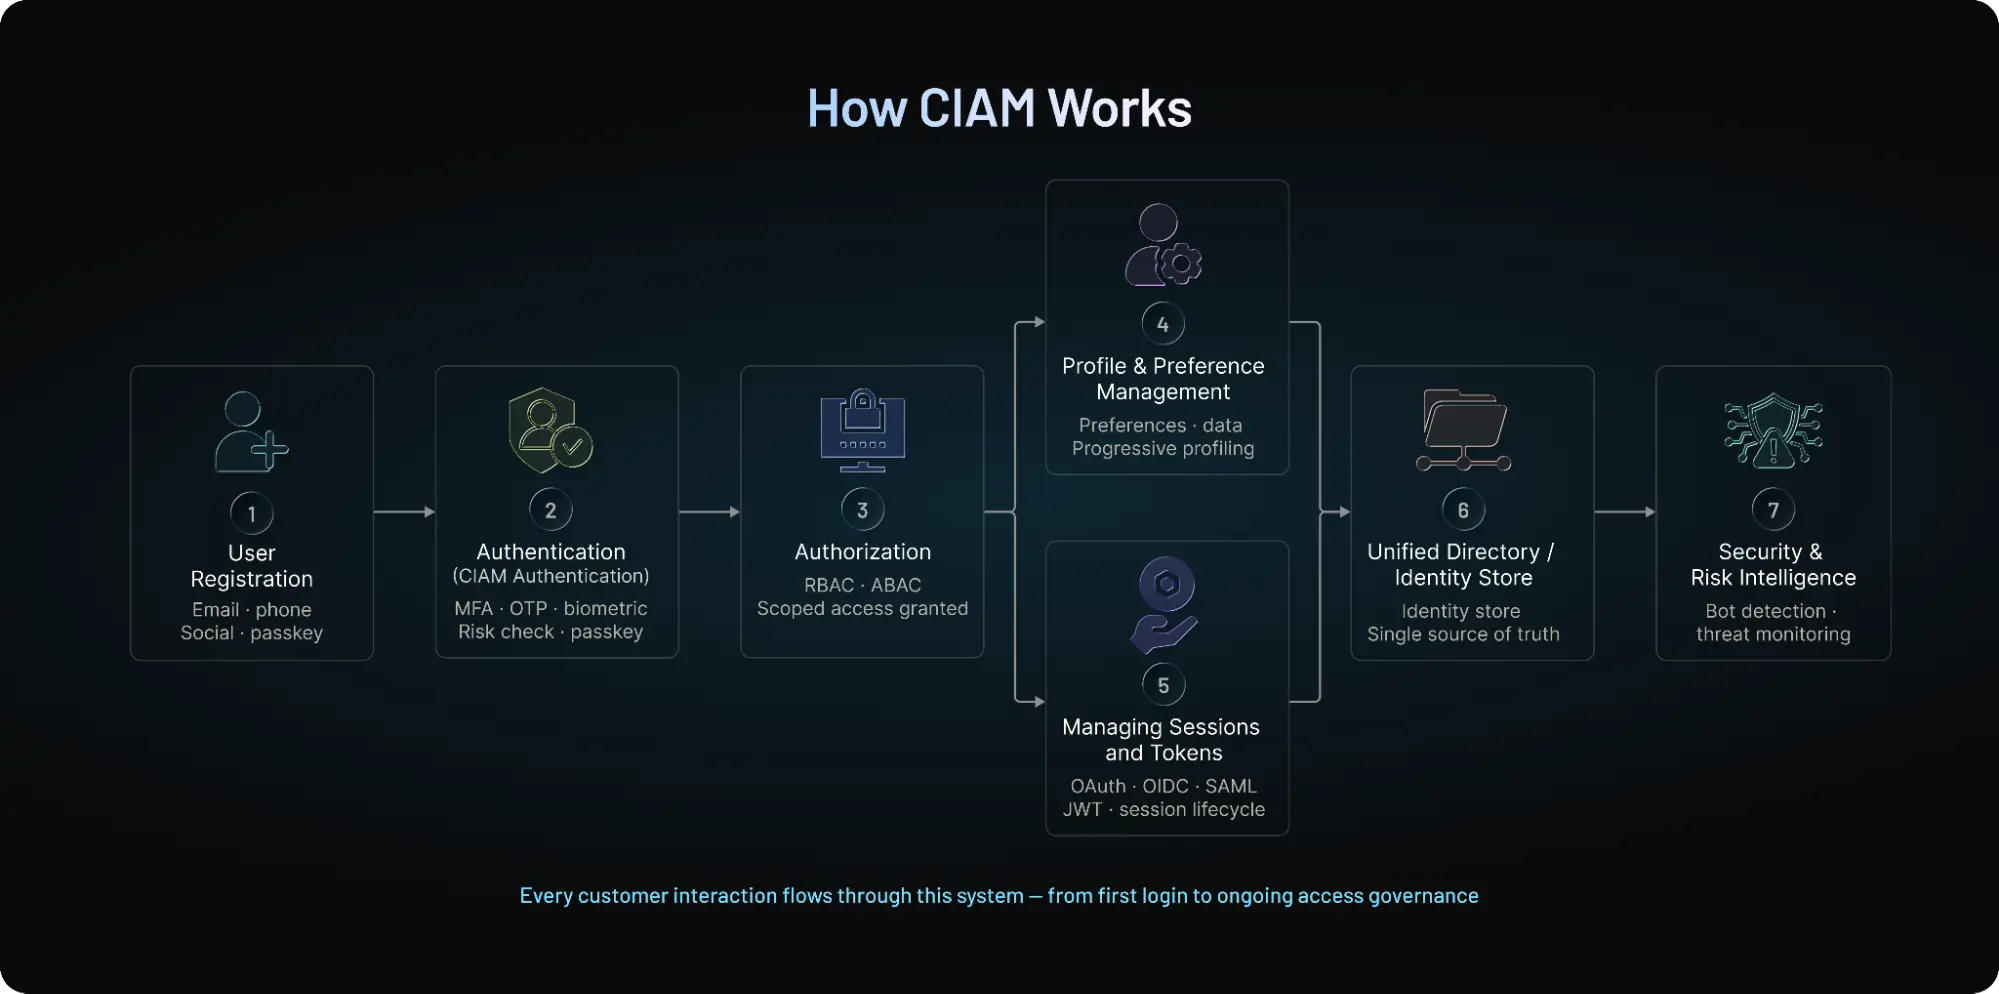
A modern CIAM architecture can also include:
-
Social identity providers
-
Passwordless authentication
-
Passkeys
-
Profile management
-
Consent and preferences
-
Progressive profiling
-
Risk-based authentication
-
Fraud and bot protection
-
APIs and SDKs
-
Customer data integrations
The architecture must support both security and customer experience.
CIAM vs IAM: What About B2B Users and Partners?
The distinction becomes less straightforward when the users are external businesses rather than individual consumers.
Consider:
-
A distributor portal
-
A supplier application
-
A reseller portal
-
A franchise management system
-
A B2B SaaS application
-
A customer administration portal
These users aren't employees, but they aren't necessarily traditional B2C consumers either.
This is where B2B identity and CIAM capabilities become important.
A B2B application may require:
-
Organization-based identity
-
Multi-tenancy
-
Per-organization roles
-
Delegated administration
-
SSO through SAML or OIDC
-
Just-in-time provisioning
-
SCIM
-
Organization-level authorization
-
Adaptive MFA
-
Audit logs
So the question isn't always simply:
IAM or CIAM?
For some organizations, the identity architecture needs to support workforce identities, consumer identities, and external business identities across different applications.
When Should You Use IAM?
IAM is generally appropriate when you need to:
-
Manage employee identities
-
Secure internal applications
-
Control workforce access
-
Enforce least-privilege access
-
Automate provisioning and deprovisioning
-
Enable enterprise SSO
-
Manage privileged access
-
Support workforce compliance requirements
Example
A manufacturing company uses IAM to manage employee access to:
HR → ERP → CRM → Collaboration Tools → Internal Applications
The identity system is centered on the workforce and the organization's resources.
When Should You Use CIAM?
CIAM is appropriate when you need to:
-
Manage customer identities
-
Build customer-facing applications
-
Support large external user populations
-
Provide flexible registration and login
-
Offer social login or passwordless authentication
-
Support passkeys
-
Manage customer profiles and preferences
-
Manage consent and privacy
-
Protect against account takeover, bots, and other identity-related threats
-
Provide a consistent identity experience across web, mobile, and APIs
Example
An online retailer uses CIAM to manage:
Registration → Login → Profile → Preferences → Checkout → Loyalty → Customer Support
The identity layer becomes part of the customer experience.
Can You Use IAM and CIAM Together?
Yes.
For many enterprises, IAM and CIAM are complementary rather than competing technologies.
A company may use IAM for its employees and CIAM for its customers.
For example:
Employees
IAM → Employee → Internal applications
Customers
CIAM → Customer → Website / Mobile App / APIs
The two systems can coexist because they solve different identity problems.
A retail company might use IAM to manage employee access to inventory and business systems while using CIAM to manage millions of customer accounts across its web and mobile experiences.
The same organization can therefore have different identity systems optimized for different populations.
CIAM vs IAM: Which One Does Your Application Need?
A simple way to think about the decision is to start with the user and the resource.
| Scenario | IAM | CIAM |
|---|---|---|
| Employee portal | ✓ | |
| Internal HR system | ✓ | |
| Corporate productivity applications | ✓ | |
| Customer mobile application | ✓ | |
| E-commerce website | ✓ | |
| Consumer marketplace | ✓ | |
| Patient portal | ✓ | |
| Banking customer portal | ✓ | |
| Subscription platform | ✓ | |
| Partner portal | ✓ | |
| Supplier portal | ✓ | |
| B2B SaaS application | ✓ | |
| Developer portal | ✓ |
The last few scenarios illustrate why the IAM/CIAM distinction should not be treated as an absolute binary.
The right architecture depends on who the users are, what they need to access, how the organization is structured, and what identity experience the application requires.
Why Traditional IAM Isn't Always the Right Choice for Customer Identity
Organizations sometimes try to extend an existing workforce IAM system to customer-facing applications.
That can work for certain scenarios, but customer identity introduces requirements that workforce IAM isn't necessarily designed around.
Customer-facing applications may need:
1. Consumer-scale identity
Millions of users and unpredictable authentication traffic.
2. Flexible registration
Customers should be able to create accounts through the channels and authentication methods appropriate to the application.
3. Low-friction authentication
Social login, passwordless authentication, passkeys, and adaptive authentication can reduce unnecessary friction.
4. Customer self-service
Customers may need to manage their profiles, credentials, preferences, and accounts without contacting support.
5. Privacy and consent
Customer identity systems need to account for consent, preferences, transparency, and privacy requirements.
6. Cross-channel identity
The same customer should be able to use the same identity across web, mobile, APIs, and other digital touchpoints.
7. Customer-focused security
Customer identity systems need to address threats such as account takeover, credential abuse, bots, and suspicious authentication behavior.
These requirements are why CIAM exists as a distinct category within the broader identity landscape.
Signs It's Time to Move From Workforce IAM to a CIAM Solution
Organizations sometimes extend existing workforce IAM systems to support customer-facing applications. While this can work in limited scenarios, customer identity often introduces requirements that traditional IAM platforms were not designed to address. If you're experiencing any of the following challenges, it may be time to consider a dedicated CIAM platform.
1. You Have Strong Traffic but Low Conversion Rates
Customer acquisition doesn't end when a visitor reaches your website or mobile application. Registration forms that collect too much information, password-related friction, and multi-step authentication workflows can create unnecessary barriers that cause users to abandon the process before creating an account or completing a purchase.
CIAM solutions help reduce this friction through capabilities such as: social login, passwordless authentication, passkeys, progressive profiling, and seamless account recovery.
2. You Need a Unified View of Customer Identity
Customer data often exists across multiple systems, including CRM platforms, marketing automation tools, e-commerce systems, support platforms, and analytics applications.
A CIAM platform provides a centralized identity layer that can unify customer profiles, consent records, preferences, and account data across these touchpoints.
This unified view helps organizations:
-
Deliver personalized experiences
-
Improve customer segmentation
-
Enable data-driven marketing
-
Support product development decisions
-
Connect identity data with downstream business systems
3. Customer Security Requirements Are Increasing
Customer-facing applications face threats that extend beyond traditional workforce authentication challenges. Modern CIAM platforms provide capabilities such as:
-
Adaptive or Risk-based authentication
-
Fraud detection
-
Bot mitigation
-
Account takeover protection
These controls help organizations apply stronger security measures when risk is elevated while minimizing friction for legitimate users.
4. Privacy and Compliance Have Become Business Requirements
Customer identity systems frequently manage personal information, communication preferences, and consent records. As organizations expand globally, identity platforms often need to support privacy requirements and regulations across multiple jurisdictions.
A CIAM platform can help manage:
-
Consent collection and tracking
-
Preference management
-
Self-service privacy controls
-
Data access and deletion requests
-
Audit trails and reporting
Providing customers with visibility and control over their data helps organizations build trust while supporting regulatory compliance initiatives.
5. Customer Acquisition and Retention Are Becoming More Difficult
Identity experiences play a significant role in both customer acquisition and retention. A lengthy registration process, repeated login challenges, and poor account recovery experiences can increase abandonment and reduce engagement.
Modern CIAM platforms help create smoother customer journeys through features such as:
-
Progressive profiling
-
Personalized authentication experiences
-
Social login
-
Passwordless authentication
-
Cross-channel identity consistency
Reducing friction throughout the customer lifecycle can improve engagement, increase retention, and support sustainable customer growth.
The Bottom Line
If your organization is struggling with authentication friction, fragmented customer data, privacy requirements, large-scale customer populations, or increasing security threats, a dedicated CIAM platform may provide capabilities that traditional workforce IAM solutions were never designed to deliver.
The goal is not to replace IAM, but to ensure that customer-facing applications have an identity architecture optimized for security, privacy, scalability, and user experience.
How to Choose a CIAM Platform
Once you've established that you need CIAM, the next question is which platform to use.
Don't evaluate CIAM solely by counting authentication features.
Consider the entire identity lifecycle.
1. Scalability and Performance
Can the platform handle your current identity population and future growth?
Ask:
-
How many identities can it support?
-
How does it perform during traffic spikes?
-
What availability architecture does it use?
-
Can it support global applications?
2. Authentication Options
Look for support for the authentication methods your customers actually need:
-
Passwordless
-
Passkeys
-
MFA
-
Social login
-
SSO
-
Adaptive authentication
-
Risk-based authentication
3. Customer Experience
Can you control the registration, login, account recovery, profile, and MFA experiences?
A CIAM platform shouldn't force every business into the same customer journey.
4. Developer Experience
Evaluate:
-
APIs
-
SDKs
-
Documentation
-
Webhooks
-
Extensibility
-
Custom workflows
-
Integration capabilities
The identity layer needs to fit into your application architecture rather than forcing your application to fit around the identity platform.
5. Security and Privacy
Look for:
-
Strong authentication
-
Risk detection
-
Fraud prevention
-
Consent management
-
Privacy controls
-
Audit capabilities
-
Relevant security certifications and compliance programs
6. Integration Ecosystem
Consider whether the platform integrates with the systems around identity:
-
CRM
-
CDP
-
Marketing automation
-
E-commerce
-
Analytics
-
Customer support
-
Data platforms
7. Migration and Vendor Lock-In
Identity is deeply embedded in an application.
Before choosing a platform, understand how easily you can migrate identities and whether the platform relies on open standards such as:
-
OAuth 2.0
-
OpenID Connect
-
SAML
-
WebAuthn
Migration should be part of the evaluation before implementation—not after.
Why LoginRadius for CIAM?
LoginRadius is purpose-built for customer identity rather than adapting a workforce identity platform to customer-facing use cases.
The platform is designed around the requirements that make CIAM different:
-
Customer registration and authentication
-
Social login
-
Passwordless authentication
-
Passkeys
-
MFA
-
Adaptive authentication
-
Customer profile management
-
Consent management
-
Risk-based security
-
APIs and SDKs
-
Flexible integration
-
High-scale identity management
LoginRadius' existing CIAM guidance emphasizes the same combination of scalability, customer experience, modern authentication, developer tools, privacy, and extensibility.
For organizations evaluating CIAM, the important question isn't simply whether a platform can authenticate a user.
It is whether the platform can support the entire customer identity lifecycle without forcing compromises between security, experience, scalability, and development flexibility.
Final Thoughts
IAM and CIAM share the same foundation: establish identity, authenticate users, and control access.
But the problems they solve are different.
IAM is primarily designed around workforce access, organizational security, and governance.
CIAM is designed around external identities and the intersection of security, privacy, scale, and digital experience.
That distinction becomes increasingly important as organizations operate more digital products, applications, customer portals, APIs, and partner ecosystems.
The question isn't always CIAM or IAM.
For many enterprises, it is:
How do we build an identity architecture that gives employees, customers, and external business users the right level of security and the right experience for the resources they need to access?
The answer may involve IAM, CIAM, B2B identity—or a combination of them.
What matters is choosing an identity architecture around the users, applications, security requirements, and experiences you need to support.
FAQs
Q: Is CIAM the same as IAM?
A: No. CIAM is a specialized approach to identity and access management designed primarily for customers and other external users. IAM is a broader category that commonly includes workforce identity and access management.
Q: What is the main difference between IAM and CIAM?
A: The primary difference is the identity population and the requirements around it.
IAM primarily secures workforce access to organizational resources. CIAM manages external identities while also addressing customer experience, privacy, scalability, and customer-facing application requirements.
Q: Can IAM and CIAM work together?
A: Yes. Many organizations use IAM for employees and CIAM for customers and other external users. The two systems address different identity populations and can coexist within the same enterprise.
Q: Is CIAM only for B2C customers?
A: No. CIAM can support a broader range of external identities, including customers, members, subscribers, application users, partners, and other external business users.
B2B applications may also require capabilities such as multi-tenancy, delegated administration, organization-level authorization, SSO, and SCIM.
Q: Is CIAM more secure than IAM?
A: The two are designed for different identity scenarios. CIAM isn't simply a more secure version of IAM. It is designed to address security requirements associated with external identities and customer-facing applications while also supporting a low-friction user experience.
Q: Why can't I just use workforce IAM for customers?
A: You may be able to use some workforce IAM capabilities for external users, but customer-facing applications often require additional capabilities around registration, customer self-service, identity scale, authentication choice, privacy, consent, and customer experience.
Q: What authentication methods does CIAM support?
A: Depending on the platform, CIAM can support authentication methods such as:
-
Passwords
-
MFA
-
Social login
-
Passwordless authentication
-
Magic links
-
Passkeys
-
Biometrics
-
Adaptive and risk-based authentication
Q: Do enterprises need both IAM and CIAM?
A: Many do. IAM can secure employee access to internal resources while CIAM manages customers and other external users across websites, applications, APIs, and digital services.