Brute-Force Defense on AIOHTTP app
Implement Brute-Force Defense Authentication/Login on your AIOHTTP App using LoginRadius
 AIOHTTP

 Brute-Force Defense
Built for Developers
Performs for Enterprise Scale!
Try our platform for free or talk to our CIAM expert to book a customer demo.
1.5B+
Identities
28+
Data Centers
100%
Uptime
100K
RPS Scaling
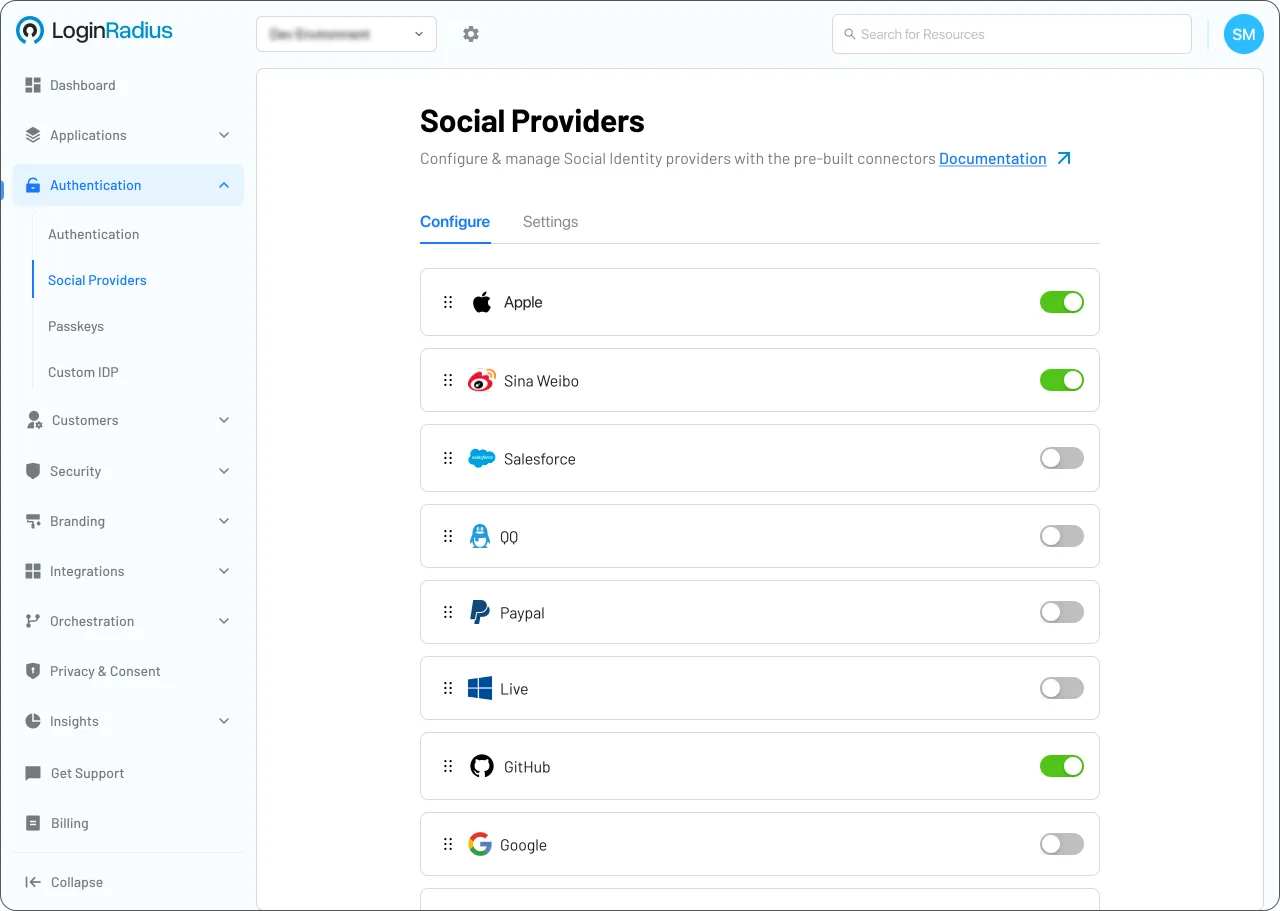
Start Brute-Force Defense Implementation Using LoginRadius Admin Console
1
Navigate to Security > User Security > Attack Protection > Brute Force Lockout in the Admin Console.
2
Set the Threshold for the maximum number of failed login or password reset attempts.
3
Define the Lockout Type (Suspend, Block, Captcha, or Security Question) and duration, then click Save.
Trusted by Developers
From Startups to Fortune 500 Companies

Interactive Resources
Detailed Case Study
You might also be interested in
Brute-Force Defense on other apps

Brute-Force Defense with Astro
Brute-Force Defense with Catalyst
Brute-Force Defense with Go
Brute-Force Defense with Prado
Other features for your AIOHTTP apps
Roles and Membership with AIOHTTP
Privacy Policy with AIOHTTP

Just-in-Time (JIT) Migration with AIOHTTP

Bot Defense with AIOHTTP
Social Identity Providers for your AIOHTTP apps
Shopify with AIOHTTP
Naver with AIOHTTP
Instagram with AIOHTTP