Brute-Force Defense on HttpRouter app
Implement Brute-Force Defense Authentication/Login on your HttpRouter App using LoginRadius
 HttpRouter

 Brute-Force Defense
Built for Developers
Performs for Enterprise Scale!
Try our platform for free or talk to our CIAM expert to book a customer demo.
1.5B+
Identities
28+
Data Centers
100%
Uptime
100K
RPS Scaling
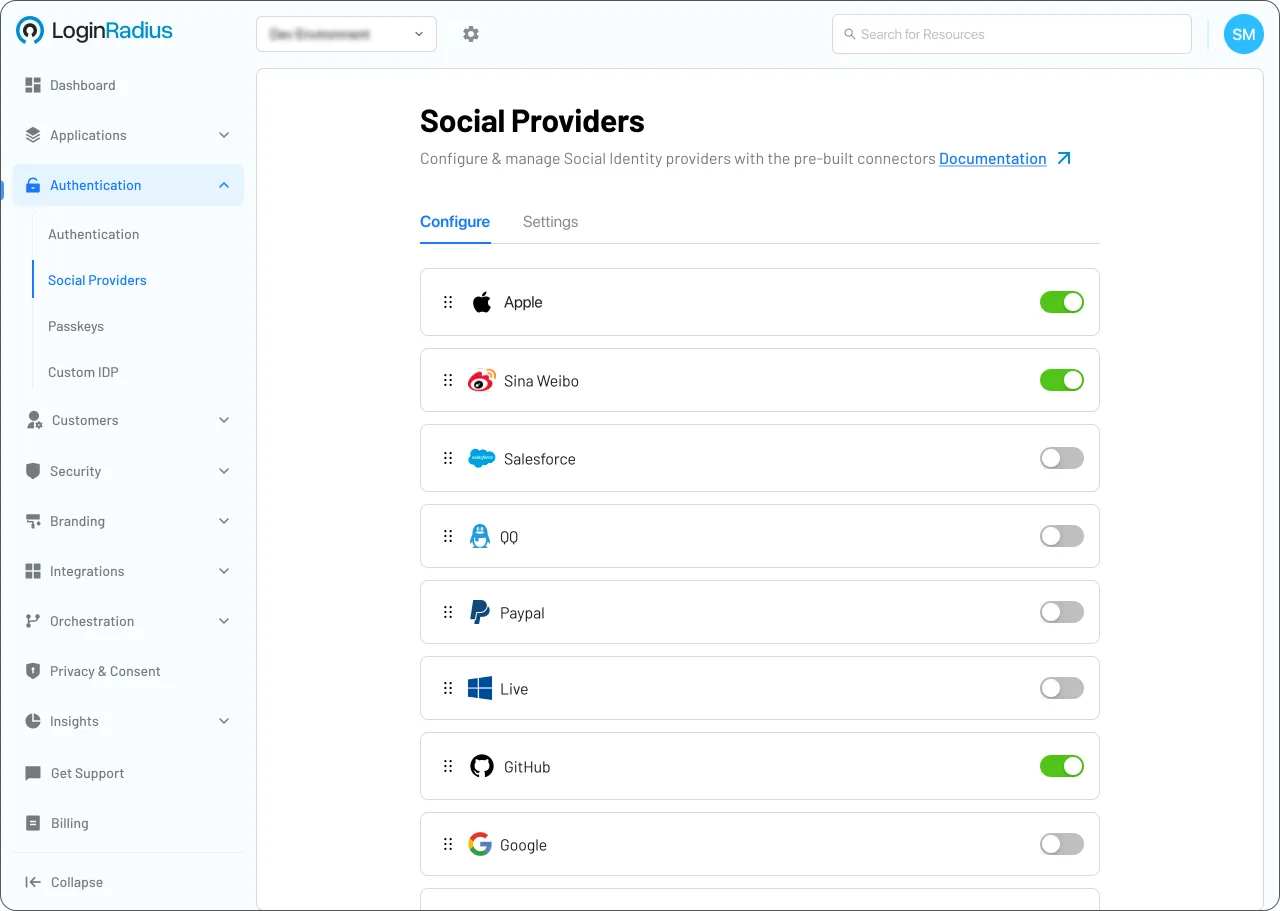
Start Brute-Force Defense Implementation Using LoginRadius Admin Console
1
Navigate to Security > User Security > Attack Protection > Brute Force Lockout in the Admin Console.
2
Set the Threshold for the maximum number of failed login or password reset attempts.
3
Define the Lockout Type (Suspend, Block, Captcha, or Security Question) and duration, then click Save.
Trusted by Developers
From Startups to Fortune 500 Companies

Interactive Resources
Detailed Case Study
You might also be interested in
Brute-Force Defense on other apps

Brute-Force Defense with Next.js
Brute-Force Defense with Blazer
Brute-Force Defense with Vue Storefront
Brute-Force Defense with Rocket
Other features for your HttpRouter apps

Data Export & Portability with HttpRouter

Machine-to-Machine with HttpRouter
Passkeys with HttpRouter

Just-in-Time (JIT) Migration with HttpRouter
Social Identity Providers for your HttpRouter apps
Twitch with HttpRouter
Odnoklassniki with HttpRouter
Azure Active Directory with HttpRouter