API Rate Limiting on JSF app
Implement API Rate Limiting Authentication/Login on your JSF App using LoginRadius
 JSF

 API Rate Limiting
Built for Developers
Performs for Enterprise Scale!
Try our platform for free or talk to our CIAM expert to book a customer demo.
1.5B+
Identities
28+
Data Centers
100%
Uptime
100K
RPS Scaling
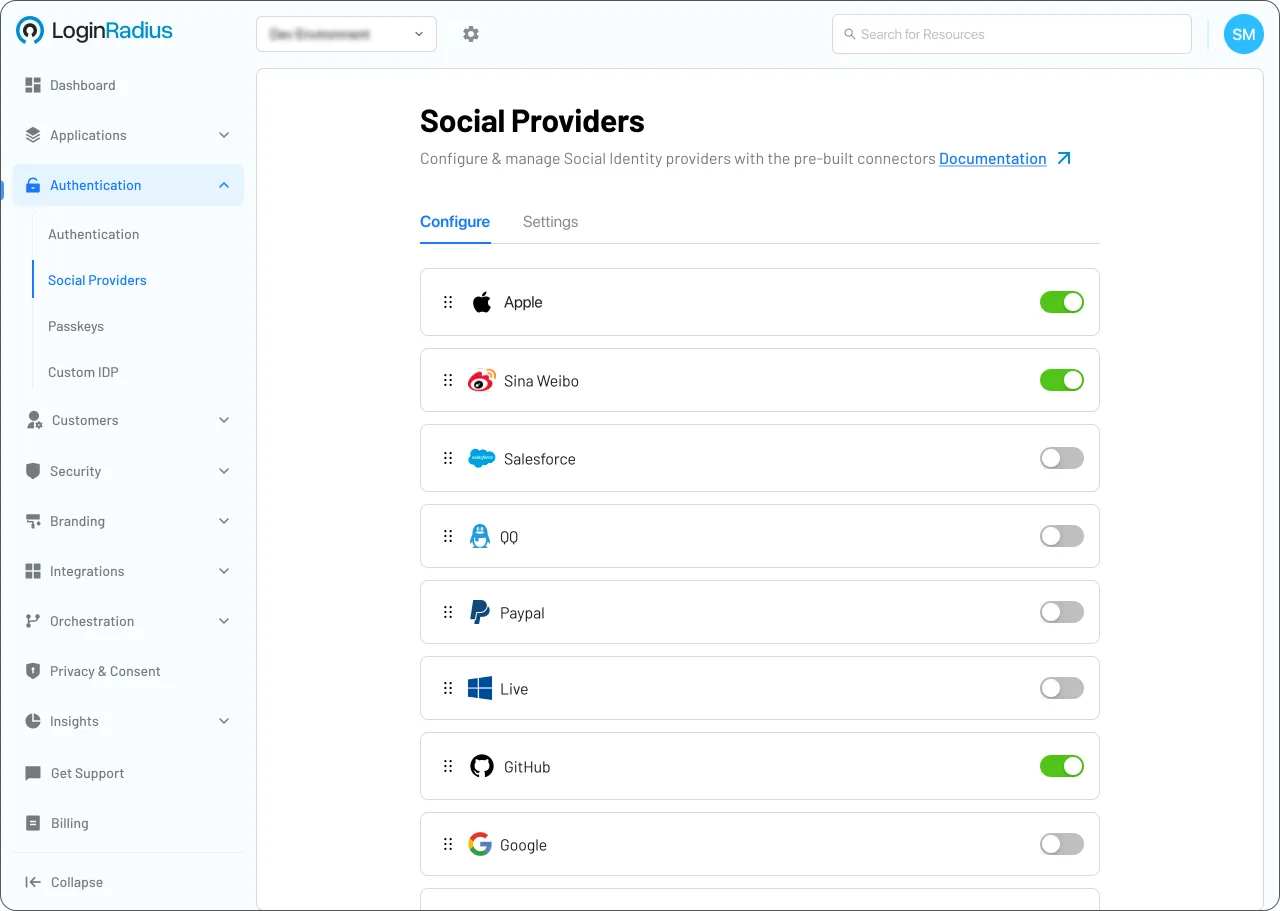
Start API Rate Limiting Implementation Using LoginRadius Admin Console
1
Monitor your current usage via Insights > Platform Analytics in the Admin Console.
2
Ensure your application handles 429 HTTP (Too Many Requests) errors using exponential backoff logic.
3
If you require higher limits than the default (e.g., 50 RPS for Production), contact your LoginRadius Account Manager or raise a support ticket.
Trusted by Developers
From Startups to Fortune 500 Companies

Interactive Resources
Detailed Case Study
You might also be interested in
API Rate Limiting on other apps
API Rate Limiting with Go
API Rate Limiting with Yii
API Rate Limiting with Symfony
API Rate Limiting with Expressjs
Other features for your JSF apps
Federated SSO with JSF

Identity Verification with JSF

Passwordless with JSF
Touch ID with JSF
Social Identity Providers for your JSF apps
Baidu with JSF
Rakuten with JSF
Naver with JSF