There was a time when AI, and especially generative AI, was just another chatbot. Smart, efficient, different - yes, but essentially a chatbot! But times have changed since then. And we have seen massive development in the "AI Agents" front. And honestly, massive would be an understatement! The developments are so huge that even developers of Anthropic and OpenAI are now expressing concerns.
And the concern is genuine. In today's world, AI agents are searching internal knowledge bases, creating tickets, triggering workflows, and interacting with third-party applications on behalf of users. So, naturally, a critical question emerges: How do you control what an AI agent is allowed to access and perform?
It introduces a new layer of complexity in the authorization front. Without clear authorization controls, a single overprivileged agent could gain access to sensitive data, execute unintended actions, or expose critical business systems.
Model Context Protocol or MCP is the standard way of communication between different AI applications. This common interface between AI hosts, clients, and servers makes it easier for organizations to connect models to real-world systems.
However, standardizing connectivity is only a part of the equation. Organizations must also ensure that every request is authenticated, authorized, and governed according to established security policies.
That is where MCP authorization comes into play. Rather than creating a completely new security model, MCP builds on proven web standards such as OAuth 2.1 to help AI agents access resources securely. The framework enables organizations to verify identities, grant permissions, enforce access controls, and limit what agents can do within connected systems.
In this guide, we'll explore how MCP authorization works, how it differs from MCP authentication, and how permissions, scopes, and access controls are enforced throughout the MCP workflow. We'll also examine common security risks, implementation best practices, and the role of centralized identity and access management in securing AI-driven ecosystems.
By the end, you'll have a clear understanding of how MCP authorization helps organizations balance AI innovation with strong security and governance.
What is Model Context Protocol (MCP)?
The Model Context Protocol (MCP) is an open standard for AI applications to connect with external systems. Think of MCP as a universal connector for AI systems. Just as USB is a standard way to connect devices, MCP is a standardized method to connect AI apps to tools, databases, business applications, and other data sources.
So, developers basically don't need to build a unique integration for every tool. They can simply use MCP to establish a common communication framework between AI models and the resources they need.
This standardization offers several advantages:
-
Faster integration with external tools and services
-
Reduced development complexity
-
Improved interoperability between AI platforms
-
Consistent security and access control mechanisms
-
Easier maintenance and governance
But more importantly, what MCP has done is, it has helped AI move beyond simple conversations. Here is an example: ChatGPT can now use MCP to log into your travel booking site, check for the lowest rates, book it on your behalf, and even initiate a payment transaction if needed. While earlier, it could just tell you the best hotels or flights at lowest rates. These capabilities transform AI models into agents that can take meaningful actions on behalf of users.
However, greater access creates greater risk. An AI agent connected to enterprise systems may encounter sensitive customer information, financial records, proprietary documents, or critical business functions. Without proper security controls, even a well-designed agent can become a potential attack surface.
This is why authorization has become one of the most important aspects of MCP deployments. While MCP standardizes connectivity, organizations still need a reliable way to determine:
-
Who is requesting access?
-
Which resources can be accessed?
-
Which actions are allowed?
-
How are permissions enforced across connected systems?
-
How can access be monitored and audited?
These questions sit at the heart of MCP authorization. But before diving into authorization, let's quickly refresh how MCP works. This will help us understand authorization better.
MCP Architecture Refresher: Host, Client, Server, and Transport
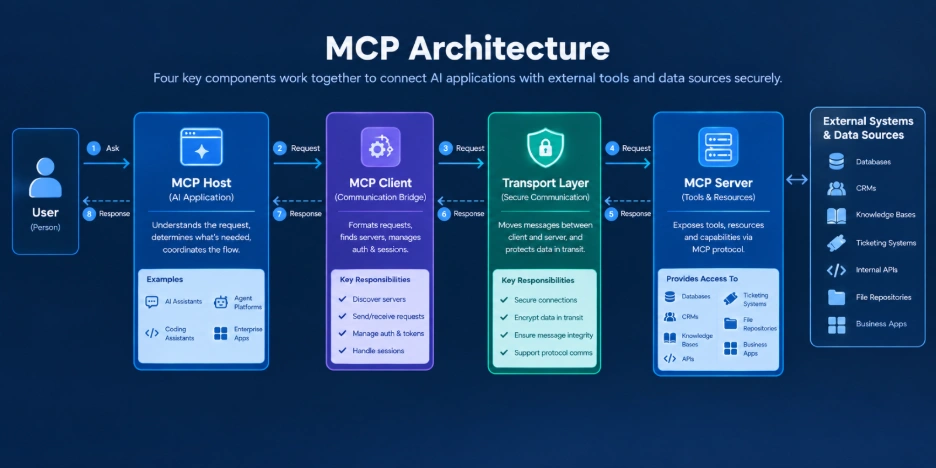
At a high level, MCP architecture consists of four main components:
-
Host
-
Client
-
Server
-
Transport layer
Each component plays a distinct role in the communication.
MCP Host
The host is the AI application that users interact with directly. When the user asks the AI app to perform a task, the host is responsible for coordinating the interaction. It also determines when external tools or data sources are needed.
For example, let's assume a user asks an AI assistant to create a support ticket. The host recognizes that the action requires access to a ticketing system and initiates the necessary MCP workflow.
Examples of hosts include:
-
AI assistants
-
Agent platforms
-
Coding assistants
-
Enterprise AI applications
-
Workflow automation tools
MCP Client
The client acts as the communication bridge between the host and MCP servers. You can think of the client as a translator. It takes requests from the host, formats them according to MCP standards, and communicates with the appropriate server.
Its primary responsibilities include:
-
Discovering available MCP servers
-
Sending requests
-
Receiving responses
-
Managing authentication and authorization flows
-
Handling access tokens and session information
MCP Server
The server exposes tools, resources, and capabilities of an application through the MCP protocol.
The MCP client working for app A first searches for available MCP servers that can fulfill its request. Once it finds a suitable server of app B from the available exposed servers, it can then query the suitable tools or resources.
An MCP server may provide access to:
-
Databases
-
CRMs
-
Knowledge bases
-
Ticketing systems
-
Internal APIs
-
File repositories
-
Business applications
Transport Layer
The transport layer is responsible for moving messages between clients and servers. Yes, it protects data while it moves between systems. However, transport security alone is not enough.
Consider a situation where an encrypted connection is established successfully. The connection may be secure, but the requesting agent could still have excessive permissions. In other words, a secure channel does not automatically mean secure access.
This distinction becomes critical when implementing defense-in-depth strategies for MCP environments.
Common responsibilities of the transport layer include:
-
Establishing secure connections
-
Encrypting data in transit
-
Ensuring message integrity
-
Supporting authorization handshakes
-
Facilitating protocol communication
Added Note - Authorization Server
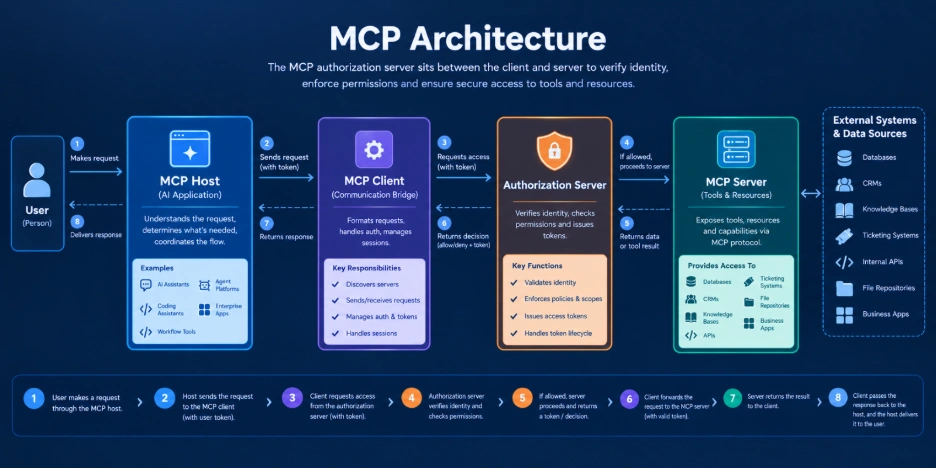
When a new request from MCP Client reaches the MCP Server, the server needs to evaluate whether the requesting client has the necessary permissions to access the requested resource or execute a specific action.
For example, an MCP server connected to a customer database may allow a support agent to view customer records. But it must prevent access to sensitive financial information. These decisions are governed by authorization policies, scopes, and permissions.
This is where MCP authorization becomes especially important. The authorization server must verify not only who is making the request but also what actions they are allowed to perform.
How These Components Work Together
A typical interaction follows a straightforward path:
-
A user submits a request through an AI host.
-
The host determines that an external tool or resource is required.
-
The MCP client sends a request to the appropriate server.
-
The server evaluates authentication of credentials and authorization permissions.
-
Access is granted or denied.
-
The server returns the result to the client.
-
The client passes the information back to the host.
-
The host delivers the response to the user.
What is MCP Authorization?
MCP authorization determines what an AI agent is allowed to access and do after identity has been verified. Most MCP implementations rely on OAuth 2.1 access tokens, scopes, and permission policies to control access to tools, resources, and APIs.
MCP Authentication vs. MCP Authorization
When discussing MCP security, two terms often appear together: authentication and authorization. While they are closely related, they solve different problems.
| MCP Authentication | MCP Authorization | |
|---|---|---|
| Purpose | Authentication answers a simple question: Who is making the request? | Authorization answers a different question: What is the requester allowed to do? |
| What It Actually Does? | Before an AI agent can access a tool, database, or API, the system must verify the identity of the user, application, or service behind the request. | Once identity has been verified, authorization determines which resources, tools, and actions are available to that user or agent. |
| Risk Without It | Without authentication, an MCP server has no reliable way to determine whether a request is coming from:* A legitimate employee* A trusted application* An approved AI agent* An unauthorized actor | All users may get access to similar levels of data and permissions. For example:* A customer support agent may be allowed to view financial records.* An AI assistant may be allowed to retrieve information and modify data without human consent. |
Even if the users successfully authenticate, they should not receive the same level of access. That is why authorization ensures that permissions align with business requirements and security policies.
Authorization in MCP is based on delegation, not impersonation. When an AI agent accesses a tool through MCP, it operates within the permissions granted to it by the user and authorization server. This ensures the agent can only perform approved actions rather than inheriting unrestricted user privileges. For a deeper discussion on delegation models for AI agents, see our guide on AI Agent Authentication.
How Authentication and Authorization Work Together in MCP
In a typical MCP workflow, authentication occurs first, followed by authorization.
The process generally follows this sequence:
-
A user signs into an AI application.
-
The user's identity is verified.
-
The AI agent requests access to an MCP resource.
-
The MCP server evaluates permissions.
-
Approved actions are allowed.
-
Restricted actions are denied.
-
This layered approach prevents systems from granting broad access simply because a request originates from a trusted identity.
MCP Authorization Workflow: How Authorization Works in MCP
Now we've explored the difference between authentication and authorization. So, let's examine how authorization actually works within an MCP environment.
Step 1: The AI Agent Requests Access
The workflow begins when a user asks an AI application to perform an action that requires access to an external resource.
For example, a user might ask an AI assistant to:
-
Retrieve customer information from a CRM
-
Search documents in a knowledge base
-
Create a support ticket
-
Query a database
-
Update a project management system
To complete the task, the AI host instructs the MCP client to connect to the appropriate MCP server.
At this point, the server must determine whether the requester is authorized to access the requested resource.
Step 2: The MCP Server Challenges the Request
If the client does not already possess a valid access token, the MCP server rejects the initial request and returns an authorization challenge.
Think of this as the server saying:
"Before I provide access, prove that you have permission."
The challenge typically contains information that helps the client discover how authorization should be performed.
This step prevents anonymous or unauthorized requests from directly interacting with protected resources.
Step 3: Authorization Server Discovery
Once the challenge is received, the MCP client must locate the appropriate authorization service.
Instead of embedding authorization directly into every MCP server, MCP separates resource access from identity and authorization management.
This separation provides several benefits:
-
Centralized policy enforcement
-
Consistent access controls
-
Easier integration with enterprise identity systems
-
Simplified permission management
The client discovers the authorization server responsible for issuing access tokens and validating permissions.
Step 4: User Authentication
Before permissions can be granted, the user's identity must be verified.
Depending on the environment, authentication may involve:
-
Single Sign-On (SSO)
-
Enterprise Identity Providers
-
Social login providers
-
Multi-factor authentication (MFA)
-
Federated identity systems
At this stage, the authorization server confirms that the requester is who they claim to be.
Remember: authentication establishes identity. Authorization comes next.
Step 5: Permission Evaluation and Consent
After authentication, the authorization system evaluates what level of access should be granted.
Several factors may influence the decision:
-
User role
-
Organizational policies
-
Application permissions
-
Requested resource
-
Requested action
-
Existing access controls
For example, an employee may be allowed to:
✅ View customer profiles
✅ Search support tickets
✅ Access internal documentation
But may not be allowed to:
❌ Modify billing information
❌ Delete records
❌ Access financial systems
The authorization server determines whether the request aligns with existing permission policies before issuing access credentials.
Step 6: Access Token Issuance
If the request is approved, the authorization server issues an access token. The access token serves as proof that authorization has already been granted.
Rather than transmitting usernames and passwords with every request, the MCP client uses the token to demonstrate its permissions.
The token typically contains information such as:
-
User identity
-
Client identity
-
Authorized scopes
-
Expiration time
-
Permission grants
Because tokens are time-limited, they reduce the security risks associated with long-lived credentials.
Step 7: Resource Access Request
Once the client receives the access token, it retries the original request. This time, the request includes the token.
The MCP server examines the token and evaluates whether the requested operation falls within the authorized scope.
The table shows an example of an AI agent connecting to a travel website on behalf of a user:
| Request | Authorized? |
|---|---|
| Read customer records | Yes |
| Search tickets | Yes |
| Delete customer accounts | No |
| Modify payment data | No |
The final decision depends on the permissions associated with the token.
Step 8: Scope Validation and Policy Enforcement
Authorization does not end when a token is presented.
The MCP server must still validate:
-
Token validity
-
Token expiration
-
Requested resource
-
Requested action
-
Scope requirements
-
Organizational policies
This validation ensures that permissions are enforced continuously throughout the workflow. Even authenticated users can be denied access if they attempt actions outside their approved scope. This principle forms the foundation of least-privilege access.
Step 9: Response Returned to the AI Application
If all authorization checks pass, the MCP server processes the request and returns the result.
The response travels back through the MCP client to the host application, which then presents the information to the user.
From the user's perspective, the interaction may appear seamless.
However, multiple authorization checks may have occurred behind the scenes before the request was approved.
MCP Permissions and Access Control
Authorization is only effective when permissions are clearly defined and consistently enforced. While access tokens establish that authorization has been granted, permissions and scopes determine the exact boundaries of that access.
For organizations deploying AI agents across multiple systems, this layer becomes critical. Without granular access controls, an agent may receive far more permissions than needed, increasing security and compliance risks.
The goal is simple: give every user, application, and AI agent access to only the resources required to perform their intended tasks.
Scopes: Defining What an Agent Can Do
Tokens become powerful when combined with scopes.
Scopes define the boundaries of access.
For example, an MCP deployment might define scopes such as:
-
customers.read
-
customers.write
-
tickets.read
-
tickets.create
-
documents.read
-
workflows.execute
When a token is issued, the authorization server associates one or more scopes with the request.
This approach enforces the principle of least privilege by giving agents only the permissions required to complete a specific task.
Why Least Privilege Matters for AI Agents
The principle of least privilege states that users and applications should receive only the minimum permissions necessary to perform their tasks.
This principle becomes even more important in AI environments.
Consider an AI agent that helps employees retrieve customer information.
To complete its role, the agent may need:
✅ Read customer profiles
✅ Search account history
But it likely does not need:
❌ Delete customer accounts
❌ Modify payment records
❌ Change user permissions
If the agent becomes compromised, encounters a prompt injection attack, or behaves unexpectedly, the damage is significantly reduced because its permissions are restricted.
In other words, strong access control helps contain failures before they become security incidents.
Resource-Level Access Control
Not all resources require the same level of protection. Organizations often classify resources according to sensitivity.
An example is given in the table below:
| Resource | Access Control Requirement |
|---|---|
| Public knowledge base | Low |
| Customer support records | Medium |
| Internal business data | High |
| Financial systems | Very High |
| Administrative controls | Critical |
An effective MCP authorization strategy should ensure that access policies align with the sensitivity of each resource.
A user who can view documentation should not automatically gain access to sensitive financial records simply because both resources are available through MCP.
Protected Resource Metadata
One challenge in distributed environments is helping clients discover how authorization should be performed.
MCP addresses this by allowing clients to retrieve information about protected resources before attempting authorization.
This metadata may include details such as:
-
Resource identifiers
-
Authorization requirements
-
Supported authentication mechanisms
-
Authorization server locations
-
Available security capabilities
Rather than hardcoding authorization endpoints into every application, clients can dynamically discover how access should be requested.
This improves flexibility and makes MCP deployments easier to maintain.
Token Validation and Introspection
Receiving a token is not enough. The MCP server must determine whether the token can still be trusted.
During validation, the server may verify:
-
Token signature
-
Expiration status
-
Issuing authority
-
Granted scopes
-
Revocation status
-
Audience restrictions
If the token fails validation, access is denied.
This process protects against common threats such as:
-
Expired credentials
-
Forged tokens
-
Replay attacks
-
Unauthorized scope escalation
As a result, authorization remains continuously enforced rather than being checked only once during login.
Dynamic Authorization Decisions
One important aspect of MCP environments is that authorization decisions may change over time.
For example:
-
An employee changes departments.
-
A project access policy is updated.
-
Sensitive data classifications change.
-
An administrator revokes permissions.
A user's identity may remain unchanged, but their access rights can evolve.
Modern authorization systems address this by performing policy evaluations dynamically instead of relying solely on static permissions.
This becomes especially important for AI agents because their access needs can vary across workflows and business contexts.
Why OAuth Is a Natural Fit for MCP
The MCP ecosystem relies heavily on concepts already proven at an internet scale.
OAuth provides several benefits for AI-driven systems:
-
Delegated authorization
-
Short-lived credentials
-
Fine-grained permission controls
-
Broad ecosystem support
-
Integration with enterprise identity providers
-
Centralized access management
Rather than inventing a new authorization framework for AI interactions, MCP builds on security practices that organizations already use to protect APIs, cloud services, and enterprise applications.
This reduces adoption barriers while improving security consistency across environments.
How OAuth 2.1 Powers MCP Authorization
MCP defines how AI applications communicate with tools and resources, but it doesn't define how users authenticate or how permissions are granted. That's why MCP relies on OAuth 2.1.
Instead of sharing usernames and passwords with every MCP server, the user authenticates with a trusted identity provider, which then issues an access token. The MCP client presents that token whenever it needs to access protected tools or resources.
This creates a delegated authorization model where:
-
The user remains in control.
-
The AI agent acts on behalf of the user.
-
The MCP server trusts the token, not the AI agent itself.
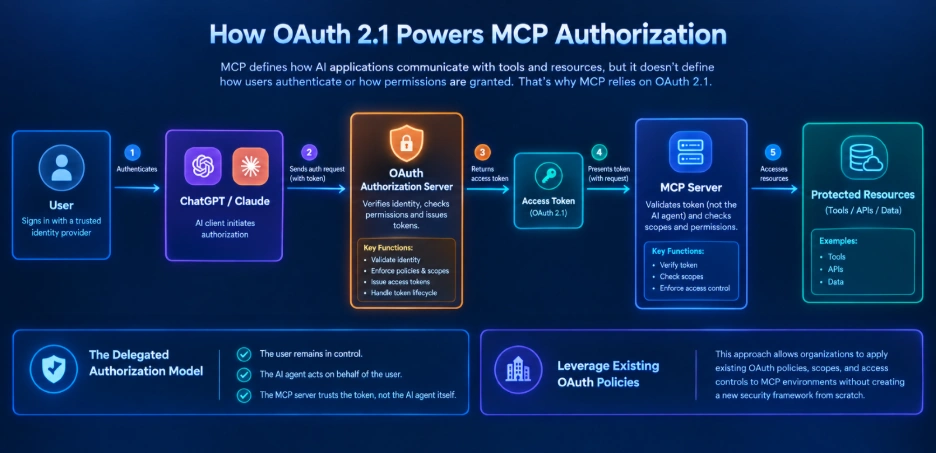
This approach allows organizations to apply existing OAuth policies, scopes, and access controls to MCP environments without creating a new security framework from scratch.
Read More - OAuth 2.0 vs OAuth 2.1: What Changed?
Why PKCE Is Critical for MCP Clients
Most MCP clients are public applications such as AI assistants, desktop tools, IDE extensions, and agent frameworks. Unlike traditional web servers, these clients cannot securely store confidential credentials.
This creates a security challenge. If an authorization code is intercepted during the OAuth flow, an attacker could potentially exchange it for an access token.
PKCE (Proof Key for Code Exchange) solves this problem.
Before the authorization request is sent, the MCP client generates a temporary secret called a code verifier and derives a code challenge from it.
When the authorization code is exchanged for an access token, the client must present the original verifier.
If the verifier doesn't match the original challenge, the request is rejected.
For MCP deployments, PKCE ensures that only the client that initiated the authorization request can complete the flow and obtain a token.
Building a Secure MCP Server with OAuth 2.1
Let's say you're a developer building a CRM platform. You've decided to expose part of your application through an MCP server so AI assistants like ChatGPT or Claude can interact with customer records.
Your MCP server exposes three tools:
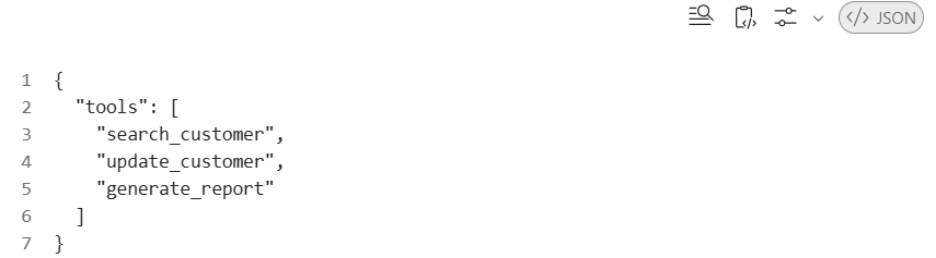
At this point, the functionality works. An MCP client can discover the tools and invoke them.
The problem is authorization.
How does your MCP server know:
-
Which user is behind the request?
-
Whether the AI agent is acting on behalf of that user?
-
Which tools the user is allowed to access?
Without authorization, any connected agent could potentially invoke every available tool.
Step 1: Reject Unauthenticated Requests
Suppose ChatGPT attempts to invoke the search_customer tool.
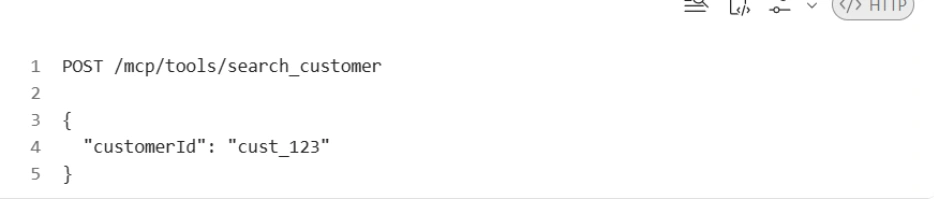
Since no access token is present, the MCP server responds with HTTP/1.1 401 Unauthorized
At this stage, the MCP server is essentially saying: "Before I allow access to customer data, prove who you are."
Step 2: Authenticate the User
The MCP client redirects the user to an OAuth authorization server. After successful authentication, the authorization server issues an access token.
A simplified token payload might look like:
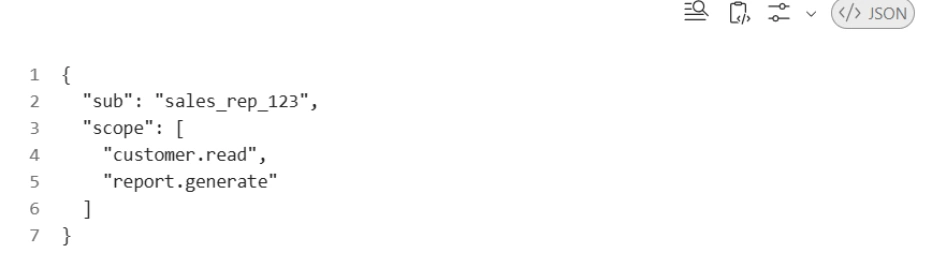
The token now carries both identity and permissions.
Step 3: Call the Tool With the Access Token
The MCP client retries the request.
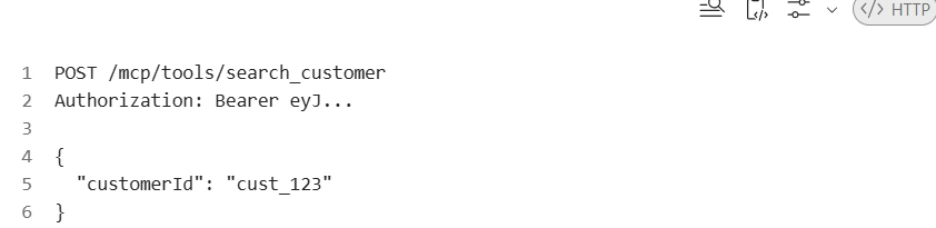
The MCP server validates the token and checks whether the required scope exists.
Pseudo-code:
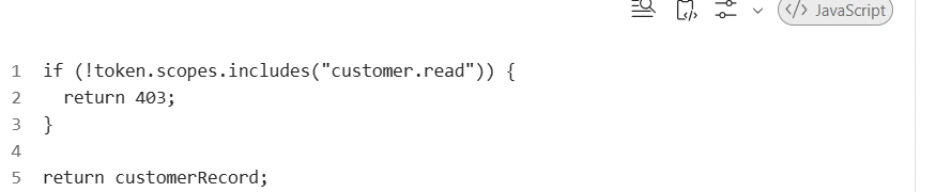
Since the scope is present, access is granted.
Step 4: Enforce Tool-Level Permissions
Now suppose the AI assistant attempts to update a customer record.
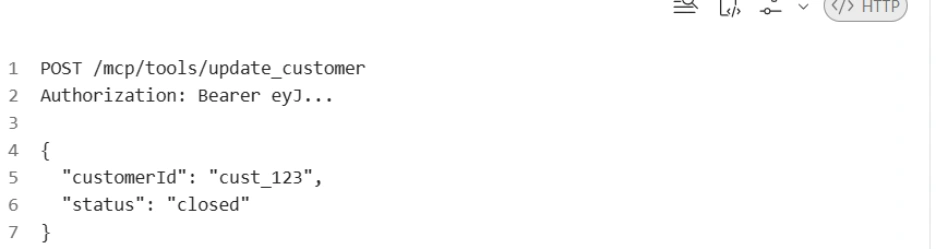
Your MCP server checks for: customer.write
However, the token only contains:
-
customer.read
-
report.generate
So, the request is denied with HTTP/1.1 403 Forbidden
This is the critical difference between authentication and authorization. The user is authenticated. The token is valid. The client is trusted. But the requested action exceeds the granted permissions. That's exactly what a secure MCP authorization implementation should do.
Transport Security vs. Tool-Level Authorization
As organizations adopt MCP, securing access is no longer just about verifying user identities or issuing access tokens. A secure MCP deployment requires protection at multiple layers.
This approach is commonly known as defense in depth. Rather than relying on a single security control, organizations implement several layers of protection that work together to reduce risk.
In MCP environments, two of the most important layers are:
-
Transport security
-
Tool-level authorization
Although they are often discussed together, they address completely different security concerns.
What Is Transport Security?
Transport security protects data as it moves between systems.
Whenever an MCP client communicates with an MCP server, information travels across a network. During this exchange, attackers may attempt to intercept, modify, or impersonate communications.
Transport security helps prevent these threats by ensuring:
-
Data remains encrypted in transit
-
Messages cannot be easily tampered with
-
Clients communicate with legitimate servers
-
Sensitive information is protected from interception
Without transport security, even a well-designed authorization framework could be compromised because attackers might gain access to credentials, tokens, or confidential business data while it is being transmitted.
Think of transport security as securing the road that information travels on.
Why Transport Security Alone Isn't Enough
A common misconception is that encrypted communications automatically mean secure access.
Consider the following example:
An AI agent successfully establishes a secure connection to a CRM system. The connection is encrypted. The server is verified. No attacker can intercept the traffic.
However, the agent still possesses permission to:
-
View customer records
-
Export account data
-
Modify account information
-
Delete customer entries
The communication channel is secure, but the permissions may be excessive. Transport security protects the connection. It does not determine whether the agent should be allowed to perform a particular action. This is where authorization becomes essential.
What Is Tool-Level Authorization?
Tool-level authorization controls what an agent can do after access has been granted. In MCP environments, servers expose capabilities through tools.
Examples include:
-
Search customer records
-
View invoices
-
Generate reports
-
Create support tickets
-
Update CRM entries
-
Trigger workflows
-
Execute automations
Each tool represents a potential action on enterprise resources.
Rather than granting blanket access to all available tools, organizations should evaluate permissions at the individual tool level.
For example: Customer Support Agent can
✅ Search Customer Records
✅ View Customer Profiles
✅ Create Support Tickets
But it cannot
❌ Delete Customer Accounts
❌ Modify Billing Information
❌ Manage User Permissions
Even if the agent is authenticated and connected through a secure encrypted channel, authorization policies can still restrict sensitive operations.
Implementation Steps: Adding Authorization to an MCP Server
Building an MCP server is relatively straightforward. Securing it is where things become challenging. And as discussed multiple times before, you need to connect it to an authorization server for this purpose.
Let's walk through the key components required to add authorization to an MCP server.
Step 1: Decide The Resources That Need Authorization
The first step is deciding which resources and tools require authorization.
For example, an MCP server may expose:
-
search_customers
-
create_ticket
-
generate_report
-
update_crm_record
-
approve_payment
Not every user or AI agent should have access to every tool.
Before exposing capabilities through MCP, define:
-
Which tools are available?
-
Which permissions are required?
-
Which operations are read-only?
-
Which operations modify data?
-
Which operations are considered sensitive?
This forms the foundation of your authorization model.
Step 2: Use an OAuth Authorization Server
MCP servers should not manage user credentials directly.
Instead, they should trust a dedicated authorization server responsible for:
-
User authentication
-
Identity verification
-
Token issuance
-
Scope management
-
Consent handling
-
Token revocation
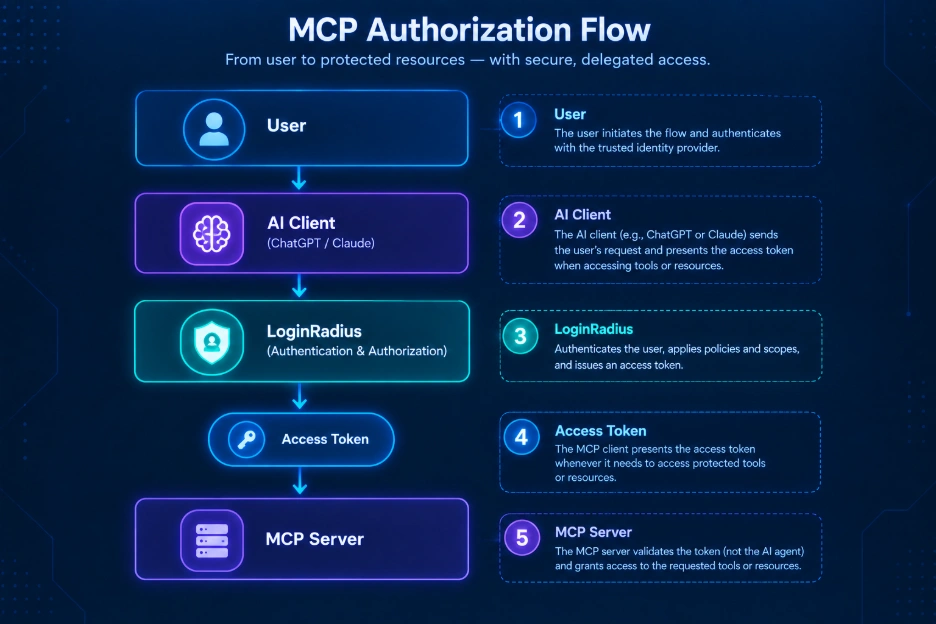
In a LoginRadius-powered deployment, LoginRadius acts as the authorization server.
The authentication flow typically looks like this:
Step 3: Authenticate the User
When the AI client attempts to access a protected MCP server, the user is redirected to authenticate.
Depending on organizational requirements, LoginRadius can support:
-
Username/password authentication
-
Single Sign-On (SSO)
-
Social login
-
Multi-factor authentication (MFA)
-
Passkeys
After successful authentication, LoginRadius issues an access token that represents the authenticated user.
At this point, the MCP server knows who the user is. The next challenge is determining what they are allowed to do.
Step 4: Issue Scoped Access Tokens
Not all tokens should grant the same permissions.
Instead, access should be defined through scopes.
For example:
-
mcp:resource:read
-
mcp:tool:list
-
mcp:tool:invoke:search_customers
-
mcp:tool:invoke:create_ticket
These scopes define exactly what an AI agent can access and execute.
A customer support assistant might receive:
-
mcp:resource:read
-
mcp:tool:invoke:create_ticket
While an administrator might receive additional permissions. This approach supports least-privilege access by ensuring agents receive only the permissions they need.
Step 5: Validate Tokens on Every Request
Authorization should not be treated as a one-time event. Every request sent to an MCP server should be validated.
Before executing a tool, the MCP server should verify:
-
Token authenticity
-
Token expiration
-
Issuing authority
-
Scope requirements
-
Permission grants
Step 6: Add Tool-Level Authorization
Many organizations stop at token validation. That is a mistake. A valid token only proves that authorization exists. The MCP server must still determine whether the requested tool should be accessible.
Step 7: Support Downstream API Access
In many deployments, the MCP server is not the final destination.
A request may require access to:
-
Internal APIs
-
Databases
-
CRM systems
-
Payment platforms
-
External SaaS applications
Passing the original user token directly to downstream systems can create security challenges.
Instead, organizations should use token exchange to create new short-lived tokens with more restricted permissions.
This approach ensures downstream services receive only the access required for the specific operation being performed.
Real-World Example: Flight Booking Assistant
Imagine a customer uses ChatGPT to book a flight.
The actors involved are:
-
MCP Client: ChatGPT
-
MCP Server: Airline Platform
-
Authorization Server: LoginRadius
The workflow looks like this:
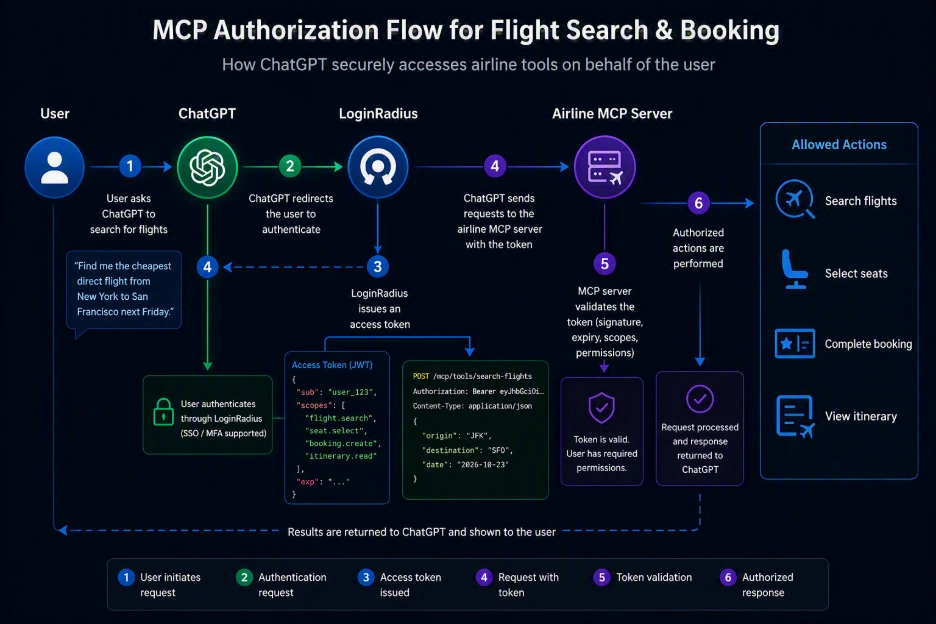
The MCP server ensures ChatGPT can only perform actions on behalf of that authenticated user. Without authorization controls, the AI agent could potentially access booking information associated with other users.
Authorization Best Practices for MCP Servers
As MCP adoption grows, several best practices are emerging.
Always:
✅ Use OAuth 2.1 and OIDC
✅ Issue short-lived tokens
✅ Validate every token
✅ Apply least-privilege permissions
✅ Restrict access at the tool level
✅ Enable auditing and monitoring
✅ Implement token revocation mechanisms
✅ Use MFA for sensitive operations
✅ Regularly review permission assignments
Avoid:
❌ Long-lived tokens
❌ Shared credentials
❌ Broad administrative scopes
❌ Hardcoded API keys
❌ Unrestricted tool access
❌ Missing audit trails
Top MCP Authorization Security Risks and Mitigation Strategies
As AI agents become more capable, MCP servers are increasingly being connected to business-critical systems, customer data, internal APIs, and automated workflows. While this unlocks powerful new use cases, it also expands the attack surface.
The challenge is not simply authenticating users. Organizations must ensure that agents cannot abuse permissions, access unauthorized resources, or perform actions outside their intended scope.
The good news is that most MCP security risks can be mitigated with strong identity, authorization, and governance controls.
Let's examine the most important risks organizations should address before deploying MCP-enabled applications in production.
1. Overprivileged Agents
One of the most common authorization mistakes is granting AI agents more permissions than they actually need.
For example, an ecommerce assistant may only need permission to:
-
Browse products
-
Add items to a cart
-
Track orders
However, a poorly designed authorization model might also grant access to:
-
Refund processing
-
User management
-
Payment administration
-
Customer account deletion
This creates unnecessary risk. If the agent is compromised, manipulated, or misconfigured, the impact becomes significantly larger.
Mitigation
Apply the principle of least privilege. Only grant permissions required for the task being performed.
For example:
Allowed:
-
mcp:tool:invoke:product_search
-
mcp:tool:invoke:track_order
Not Allowed:
-
mcp:tool:invoke:user_delete
-
mcp:tool:invoke:admin_access
Permissions should be reviewed regularly as agent capabilities evolve.
2. Prompt Injection Attacks
Prompt injection has emerged as one of the most discussed security risks in agentic AI.
In a prompt injection attack, an attacker attempts to influence an AI model into performing actions that were never intended by the user or application.
For example, a malicious webpage or document may attempt to instruct an agent to:
-
Reveal sensitive information
-
Access restricted resources
-
Invoke unauthorized tools
-
Ignore existing instructions
If authorization controls are weak, the agent may successfully execute those actions.
Mitigation
Never rely solely on model behavior for security. Even if an AI model receives malicious instructions, authorization policies should continue to enforce access boundaries.
Implement:
-
Tool-level authorization
-
Scope validation
-
Resource restrictions
-
Runtime policy enforcement
A prompt may suggest an action, but the MCP server should make the final authorization decision.
3. Excessive Scope Assignment
OAuth scopes are designed to limit access. However, many organizations issue overly broad scopes because they are easier to manage initially.
For example: crm.full_access
While convenient, broad scopes often grant far more privileges than an agent actually requires.
A safer alternative would be:
-
crm.contacts.read
-
crm.reports.generate
-
crm.tasks.create
Granular scopes significantly reduce the blast radius of a compromised token.
Mitigation
Design MCP-specific scopes around:
-
Individual tools
-
Individual resources
-
Specific actions
Examples include:
-
mcp:resource:read
-
mcp:tool:list
-
mcp:tool:invoke:search_customer
-
mcp:tool:invoke:create_ticket
This creates stronger permission boundaries and improves auditability.
4. Token Theft and Credential Leakage
Access tokens enable AI agents to act on behalf of users. If tokens are stolen, an attacker may gain the same permissions as the legitimate user.
Common causes include:
-
Insecure storage
-
Application logging mistakes
-
Exposed browser sessions
-
Poor token lifecycle management
The risk becomes even greater when long-lived tokens are used.
Mitigation
Organizations should:
-
Use short-lived access tokens
-
Enable token revocation
-
Rotate refresh tokens
-
Avoid storing tokens unnecessarily
-
Secure communications with TLS
Token lifecycle management is especially important for long-running AI workflows.
5. Unauthorized Downstream API Access
Many MCP servers act as intermediaries. The server receives a request from an AI client and then interacts with additional internal services.
A common mistake is forwarding the original user token directly to every downstream system. This often results in excessive permissions being propagated throughout the environment.
Mitigation
Implement token exchange and delegation patterns.
Instead of reusing the original token:
-
Validate the incoming token.
-
Exchange it for a new token.
-
Issue only the scopes required for the downstream action.
-
Set a short expiration period.
This creates stronger isolation between systems.
6. Agent Impersonation
Organizations typically focus on user identity but overlook agent identity. As AI ecosystems grow, multiple agents may interact with MCP servers simultaneously.
Examples include:
-
ChatGPT
-
Claude
-
IDE assistants
-
Internal AI copilots
-
Workflow automation agents
Without proper controls, it becomes difficult to determine:
-
Which agent initiated a request
-
Whether the agent is trusted
-
What permissions belong to the user versus the agent
Mitigation
Establish a clear identity model for both:
-
Human users
-
Non-human agents
Access tokens should contain claims that identify:
-
user_id
-
agent_id
-
agent_type
-
client_id
This improves traceability and supports stronger authorization policies.
7. Insufficient Audit Trails
A common enterprise requirement is answering questions such as:
-
Who accessed this data?
-
Which agent performed this action?
-
When was access granted?
-
Which permissions were used?
Without detailed auditing, investigating security incidents becomes difficult. This challenge grows significantly as organizations deploy more autonomous agents.
Mitigation
Implement comprehensive logging for:
-
Authentication events
-
Token issuance
-
Token refreshes
-
Consent grants
-
Permission changes
-
Tool invocations
-
Authorization failures
A strong audit trail improves compliance, incident response, and governance.
8. Lack of Consent and Delegation Controls
Many MCP workflows involve agents acting on behalf of users.
For example:
-
Booking flights
-
Purchasing products
-
Updating CRM records
-
Triggering business workflows
Users should understand:
-
What permissions are being requested
-
Which resources are being accessed
-
What actions may be performed
Without proper consent mechanisms, organizations risk over-delegating authority to AI agents.
Mitigation
Provide transparent consent experiences that allow users to:
-
Approve access
-
Reject requests
-
View granted permissions
-
Revoke access later
Delegated access should always remain under user or administrator control.
9. Long-Lived Agent Sessions
AI workflows are often continuous. Agents may execute tasks over extended periods without direct user interaction. If access tokens never expire, attackers gain a much larger window of opportunity.
Mitigation
Use:
-
Short-lived access tokens
-
Refresh token rotation
-
Token revocation capabilities
-
Session monitoring
This reduces the impact of stolen credentials and unauthorized access attempts.
Centralized Agent Governance with LoginRadius
As organizations expose MCP servers to AI agents, managing authentication and authorization across users, agents, tools, and downstream APIs quickly becomes complex.
LoginRadius MCP Auth helps address this challenge by acting as the centralized authorization layer for MCP-based applications. It enables organizations to authenticate users, issue OAuth 2.1/OIDC-compliant tokens, and enforce scoped access to MCP tools and resources.
With LoginRadius, developers can:
-
Authenticate users through SSO, social login, MFA, passkeys, and federated identity providers
-
Secure MCP servers using OAuth 2.1 and OpenID Connect (OIDC)
-
Issue short-lived, scoped access tokens for AI agents
-
Enforce least-privilege access to MCP tools and resources
-
Revoke access and manage token lifecycles centrally
-
Maintain auditability across agent-driven workflows
By centralizing identity and authorization, LoginRadius enables AI agents to act on behalf of authenticated users while ensuring every action remains within approved security boundaries.
Learn more about LoginRadius MCP Auth and how to secure MCP servers with OAuth 2.1 and OIDC.
Read more - LoginRadius Docs - MCP Auth
Conclusion
MCP is rapidly becoming the standard way for AI applications to connect with external tools, resources, and business systems. However, connectivity alone is not enough. As AI agents gain the ability to search data, trigger workflows, modify records, and perform transactions on behalf of users, authorization becomes the foundation of secure agentic experiences.
A successful MCP security strategy requires more than authentication. Organizations need strong authorization controls, scoped access tokens, least-privilege permissions, tool-level access management, auditing, and governance. Together, these controls ensure that agents can act on behalf of users without exceeding approved boundaries.
By building on proven standards such as OAuth 2.1 and OpenID Connect, organizations can secure MCP deployments using familiar identity and access management patterns. And with a centralized identity platform such as LoginRadius, they can manage users, agents, permissions, and delegated access consistently across their entire MCP ecosystem.
The result is a safer, more scalable foundation for AI-powered applications, one where agents can access the right tools, perform the right actions, and operate within clearly defined security boundaries.
FAQ
Q. What is MCP authorization?
MCP authorization is the process of controlling which tools, resources, and actions an AI agent can access through a Model Context Protocol (MCP) server. It typically uses OAuth 2.1 access tokens, scopes, and permissions to ensure agents act only within approved boundaries.
Q. How does OAuth 2.1 work with MCP?
OAuth 2.1 provides the authorization layer for MCP. A user authenticates with an authorization server, which issues an access token. The MCP client presents that token to the MCP server, which validates the token and enforces access based on scopes and permissions.
Q. Does MCP require OAuth?
No. MCP does not mandate OAuth. However, for production deployments, OAuth 2.1 is the recommended approach because it provides standardized authentication, delegated authorization, token management, consent, and scoped access control.
Q. What are MCP scopes?
MCP scopes define what an AI agent can do after authorization. Examples include reading resources, listing tools, or invoking specific tools. Scopes support least-privilege access by granting only the permissions required for a particular task.
Q. What is the difference between MCP authentication and authorization?
Authentication verifies who is making the request. Authorization determines what that user or AI agent is allowed to access and do. Authentication establishes identity, while authorization enforces permissions and access policies.
Q. Why is PKCE required in MCP?
Most MCP clients are public clients, such as AI assistants, desktop applications, and agent frameworks. PKCE protects OAuth authorization flows by preventing intercepted authorization codes from being exchanged for access tokens by unauthorized parties.
Q. How are AI agents authorized in MCP?
AI agents are typically authorized through OAuth access tokens issued on behalf of authenticated users. The MCP server validates the token, evaluates scopes and permissions, and determines whether the requested action should be allowed.
Q. What is tool-level authorization in MCP?
Tool-level authorization controls which MCP tools an agent can invoke. Even with a valid access token, an agent may be allowed to access some tools while being denied access to others based on roles, scopes, policies, or business rules.
Q. What is an MCP server?
An MCP server exposes tools, resources, prompts, or workflows to AI applications through the Model Context Protocol. It acts as the bridge between AI agents and external systems such as APIs, databases, CRMs, and business applications.
Q. What is an MCP Client?
An MCP client is the component that connects an AI application to an MCP server. It discovers available tools and resources, handles authorization flows, sends requests, and returns responses to the AI application. Examples include ChatGPT, Claude Desktop, IDE extensions, and agent frameworks when they interact with MCP servers.
Q. How does MCP support least-privilege access?
MCP supports least-privilege access through scopes, permissions, and tool-level authorization. Agents receive only the minimum privileges required to complete their tasks, reducing the risk of unauthorized actions or data exposure.
Q. What is token exchange in MCP?
Token exchange allows an MCP server to obtain a new, scoped token when calling downstream APIs on behalf of a user. This prevents over-privileged access and limits the permissions granted to internal or third-party services.
Q. Why is authorization important for AI agents?
AI agents can access data, trigger workflows, and perform actions across multiple systems. Authorization ensures they operate only within approved permissions, helping prevent unauthorized access, excessive privileges, and accidental misuse of sensitive resources.