Identity and Access Management (IAM) is a core discipline for any enterprise IT, as it is inseparably linked to the security and sustainability of companies. It refers to the collection of security frameworks, policies and technical tools used to manage digital identities.
More and more businesses are storing their confidential customer and employee data electronically, which makes it important to ensure that these data remains secure. One might hear a lot of terms like "Users," "roles," "access" concerning identity and access management. So, let's break down a couple of the core terms:
-
Identity: Identity implies how you are represented and digitally documented online, sometimes through social login, work email address, or personal email ID.
-
Access: Access refers to determining that the right user can access the right resource securely inside a network, at the right time.
This is majorly what an ideal identity and access management strive to provide.
What Is Identity and Access Management in Cybersecurity
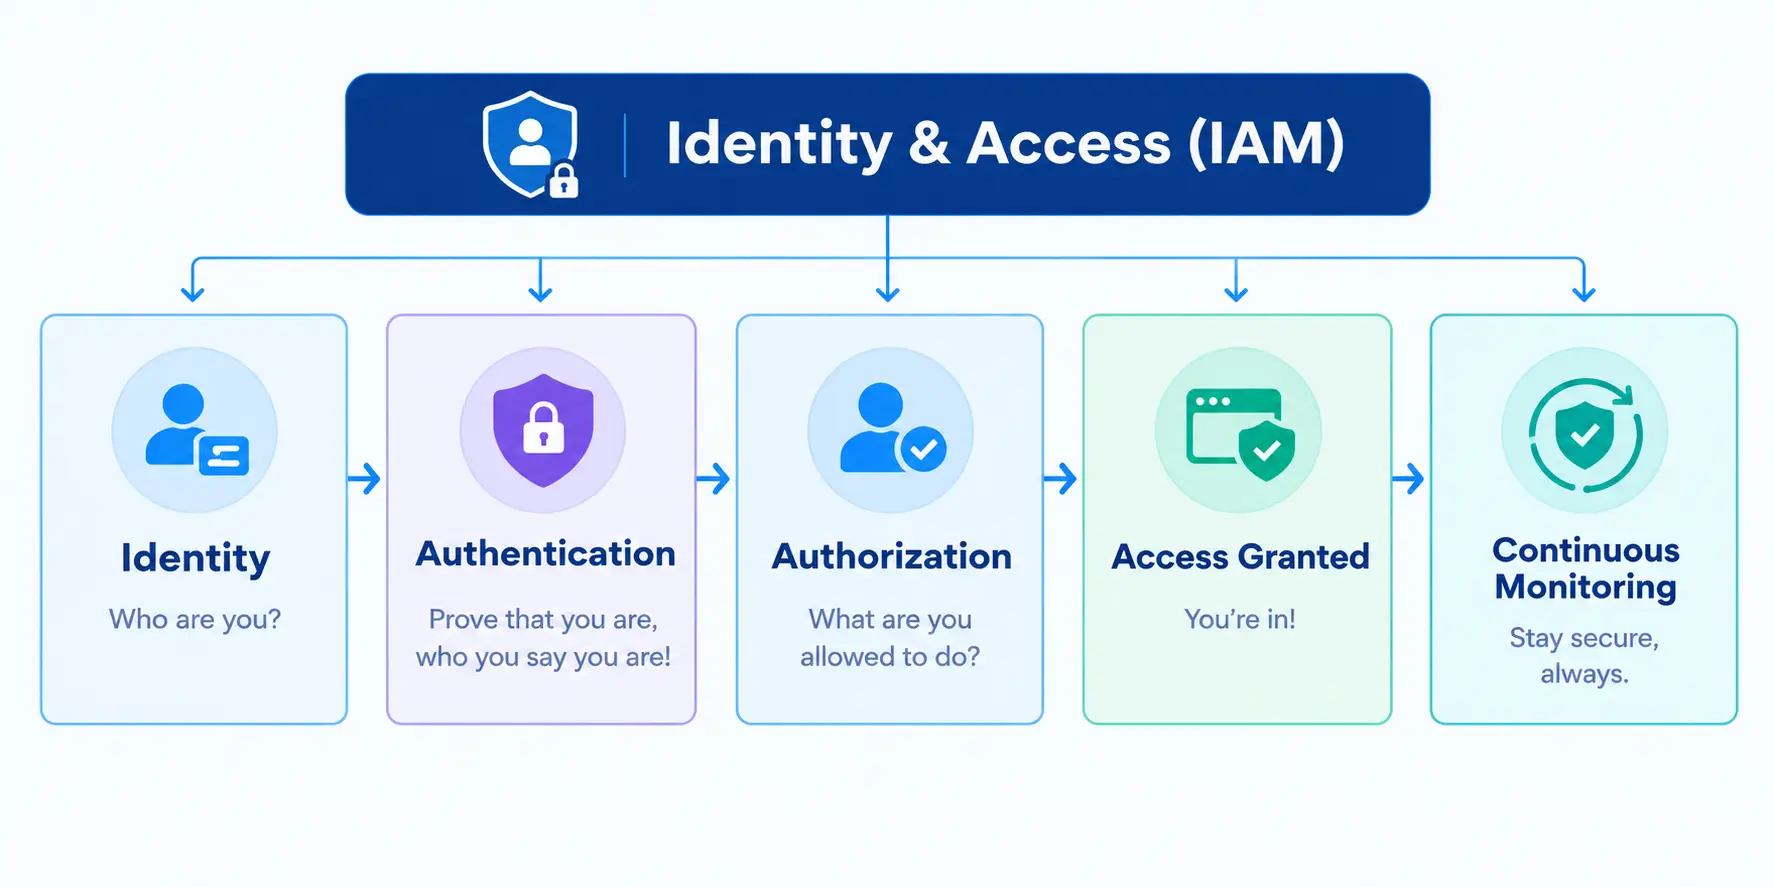
Identity and Access Management in cybersecurity refers to the security framework and disciplines for managing digital identities. It regulates the responsibilities and access privileges associated with individual consumers and the conditions in which such privileges are allowed or denied.
In simpler terms, IAM encompasses:
-
The provisioning and de-provisioning of identities in the IAM system: Creating user profiles upon onboarding and removing them when offboarding.
-
Securing and authenticating identities: Verifying the users to see if they are who they claim to be.
-
Authorizing access: Granting access to resources or allowing them to perform only eligible actions.
-
Incorporating the correct levels of protection and access for sensitive data.
IAM includes tools like two-factor authentication, multi-factor authentication, single sign-on, and privileged access management. These tools can store identity and profile data safely.
They also comply with data governance functions to ensure that only appropriate and relevant information is being shared.
What Are the Key IAM Terms
Here are some of the key terminologies that you will encounter while working in identity and access management.
| Terms | Definition | Example |
|---|---|---|
| Entity | A person, organization, device, application, or other objects that can be identified and managed within an IAM system. | An employee, customer, business partner, or applications. |
| Identity Analytics | Use identity, authentication, authorization, and behavioral data to identify patterns, anomalies, and potential security risks. | Ability to detect that a user is logging in from an unusual location, etc. |
| Managed Policy | A defined set of rules that determines which users, groups, or roles can access specific resources and what actions they are allowed to perform. | Privacy policy, Terms and Conditions etc. |
| Multi-Factor Authentication (MFA) | MFA verifies a user's identity using two or more authentication factors, such as something they know, they have, they are or something they do. | Factor 1: Username and Password Factor 2: a code from an authenticator app or a biometric factor. |
| Principal | A principal is an entity that requests access to a resource. It can be a human user, application, service, or automated system. | An employee requesting access to a payroll application is a principal making an access request. |
| Privileged Account Management (PAM) | PAM is the practice of controlling, monitoring, and auditing accounts that have elevated access to sensitive systems and resources. | A system administrator. |
| Risk-Based Authentication | Risk-based authentication evaluates contextual signals and assigns a risk level to an authentication attempt before deciding whether to allow access, request additional verification, or block the user. | A login from a familiar device may be allowed normally, while a login from an unfamiliar device and unusual location may trigger MFA. |
| Single Sign-On (SSO) | SSO allows users to access multiple applications using a single set of credentials or authentication session, reducing the need to authenticate separately with each application. | An employee signs in once with their corporate identity and can then access Salesforce, Slack, and other authorized applications without logging in again. |
| User Provisioning | User provisioning is the process of creating user accounts and assigning the appropriate access privileges when users need access to applications or resources. | When a new employee joins the company, their identity is created and they are automatically given access to the applications required for their role. |
How IAM Works
Identity and access management systems perform three main tasks viz. identification, authentication, and authorization. In other words, IAM functions to provide the right people access to devices, hardware, software applications, or any IT tool to perform a specific task.
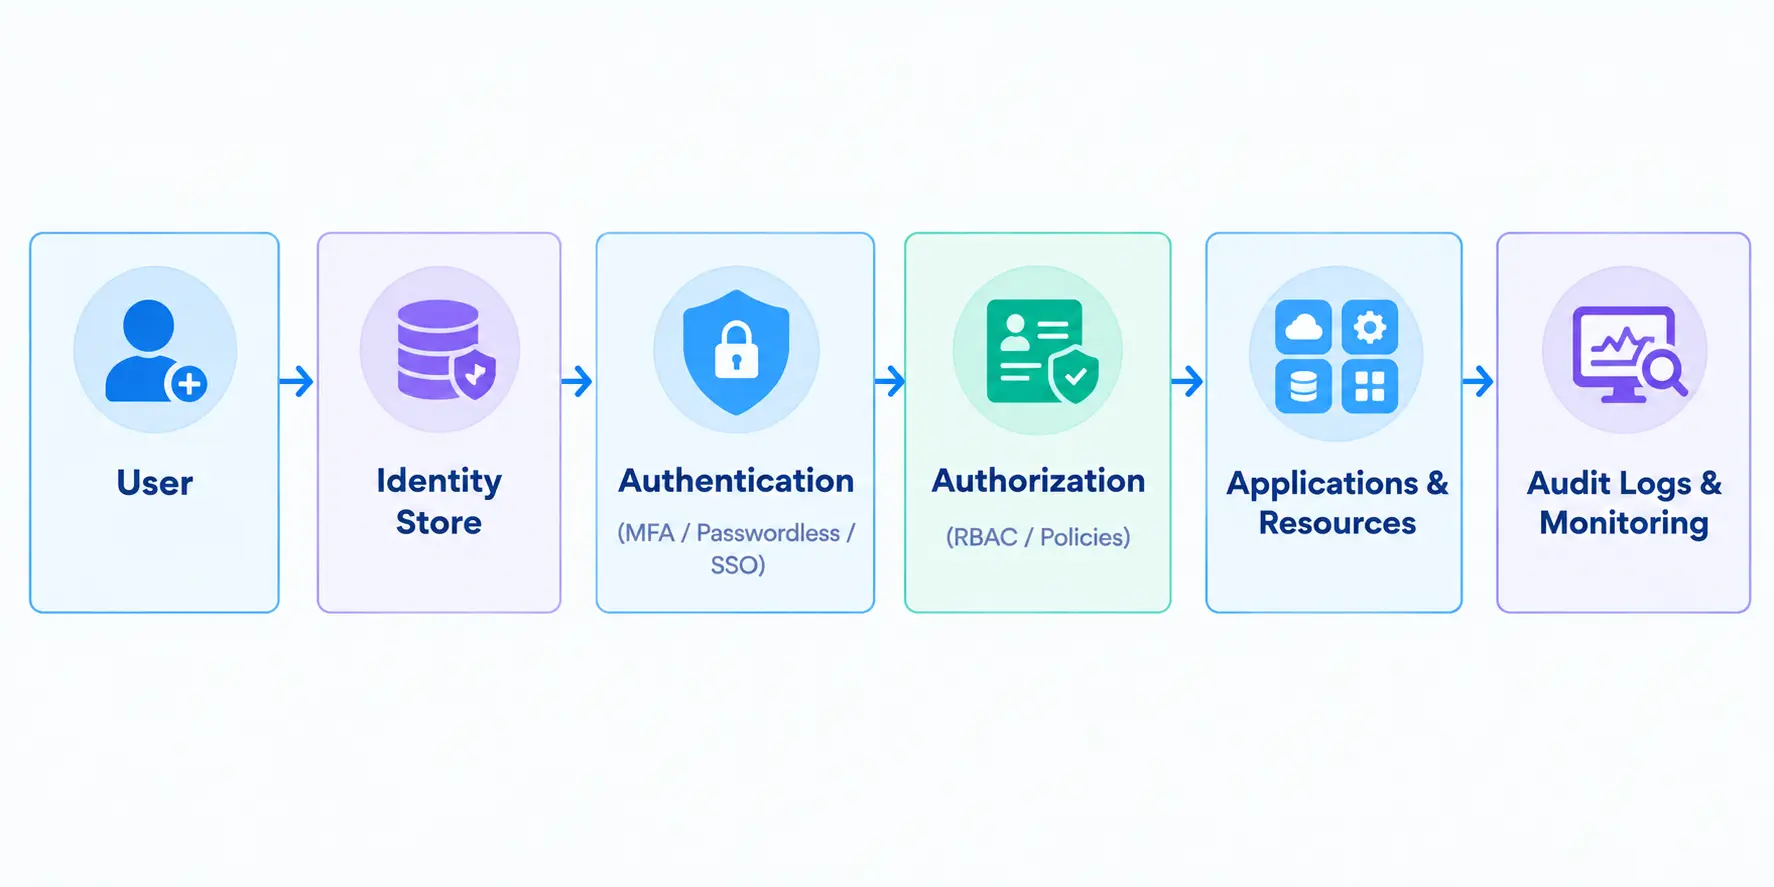
All IAM includes the following core components:
-
A database that includes the identities and access rights of users.
-
IAM tools to provision, monitor, change and remove access privileges.
-
A framework for auditing login and access history.
The list of access rights must be up-to-date all the time with the entry of new users or the change of roles of current users. In an enterprise, the responsibilities of identity and access management typically come under IT or departments that handle data processing and cybersecurity.
The key functionalities of an IAM
-
It manages identities: IAM creates, modifies, and deletes users. It also integrates with one or more other directories and synchronizes with them.
-
It provisions/de-provisions users: Once a user seeks permission to enter a system, IAM specifies which resource the user has access to and what level of access (like editor or viewer) based on their roles in the organization. On the contrary, when a user leaves the organization, IAM deprovisions from all the systems they have access to. After all, an ex-employee still having access to an organization's resources can have serious security implications.
-
It authenticates users: IAM authenticates users using tools like multi-factor authentication and adaptive authentication when they request access.
-
It authorizes users: After authenticating, IAM authorizes access to specific apps and resources based on predefined provisioning.
-
It provides reports: IAM reports help organizations identify possible cybersecurity threats, and strengthen their safety processes and bring them under global compliances.
-
It offers single sign-on: IAM allows consumers to access any connected web properties with a single identity. SSO adds security to the process of authentication and makes it even easier and faster to access resources.
Types of IAM
The major types are: Traditional IAM or Workforce IAM, Customer Identity and Access Management (CIAM), and B2B IAM. Each serves a different identity population and is designed around different access requirements, security considerations, and user experiences.
Understanding these different types of IAM is important because the identity requirements of an employee are very different from those of a customer or business partner. An employee may need access to dozens of internal applications, while a customer may need a simple and frictionless way to sign in to a website or application. Similarly, a business partner may need access to selected resources belonging to multiple organizations.
Internal Identities
Internal identities are digital identities associated with people who work within an organization. These identities typically include employees, contractors, and other workforce users who require access to an organization's internal applications, systems, networks, and data.
Internal identity management focuses heavily on controlling what employees can access based on their roles and responsibilities. For example, a member of the finance team may need access to financial applications, while an engineer may require access to development environments and source-code repositories. As employees change roles, join new teams, or leave the organization, their access privileges must also be updated.
Internal identities are generally managed through enterprise directories and identity providers. Organizations commonly use capabilities such as Single Sign-On (SSO), Multi-Factor Authentication (MFA), role-based access control (RBAC), user provisioning, de-provisioning, and privileged access management to secure these identities.
Traditional IAM
Traditional IAM refers to the identity and access management systems primarily designed to manage internal workforce identities.
- These systems have historically been built around the needs of IT departments and enterprise administrators rather than external users. The primary objective is to make sure that employees have the access they need to perform their jobs while preventing unauthorized access to sensitive organizational resources. In this environment, security and administrative control are usually the primary considerations, while user experience, although important, is often secondary to organizational security policies.
For example, when a new employee joins an organization, an IAM system can create the employee's identity, provision access to the applications required for their role, enforce MFA, and provide SSO across supported applications. When the employee leaves, the organization can de-provision the identity and revoke access to those resources.
External Identities
External identities are digital identities that belong to users who are outside an organization's workforce. They can include customers, consumers, business partners, suppliers, distributors, vendors, franchisees, contractors, and other users who interact with an organization's applications or digital services.
External users cannot be managed the same way as your employees. An organization may not control their identity in the same way, and their relationship with the business will vary significantly. A customer may create an account independently, while a business partner may be invited by an administrator and receive access to specific applications or resources.
External identities therefore introduce additional requirements around identity registration, authentication, authorization, consent, privacy, self-service, and user experience. Organizations must be able to securely manage these identities without creating unnecessary friction for users.
External identity management is commonly divided into two major areas: Customer Identity and Access Management (CIAM), which focuses primarily on consumers and customers, and B2B IAM, which focuses on identities representing other businesses and organizations. LoginRadius offers platforms in external identity management space only and now also has a platform for Agentic IAM.
Customer Identity and Access Management (CIAM)
Customer Identity and Access Management, commonly known as CIAM, is an identity management approach designed specifically for managing customer and consumer identities. CIAM enables organizations to securely register, authenticate, authorize, and manage large populations of external users who interact with digital products and services.
-
Unlike traditional IAM, CIAM is closely connected to the customer experience. Customers expect to be able to create an account quickly, sign in using a preferred authentication method, and access services without unnecessary steps. Organizations therefore use capabilities such as social login, passwordless authentication, passkeys, MFA, progressive profiling, adaptive authentication, self-service account management, and consent management to create secure but frictionless experiences.
-
CIAM also needs to operate at a much larger and less predictable scale than many internal IAM environments. A consumer application may have millions of users and experience significant spikes in authentication traffic during product launches, marketing campaigns, or seasonal events.
-
Another important difference is that CIAM is often embedded directly into customer-facing applications and websites. The identity experience is therefore part of the organization's product and brand experience rather than simply an internal IT function.
-
CIAM also provides organizations with a centralized identity and profile layer. This can allow customer identity data to be securely connected with applications, customer experience platforms, analytics systems, and other business technologies while maintaining appropriate privacy and security controls.
B2B IAM
B2B IAM is designed to manage identities that belong to business customers, partners, suppliers, vendors, distributors, franchisees, and other external organizations. While B2B users are external identities, their identity requirements are fundamentally different from those of individual consumers.
-
A B2B application may need to support multiple organizations, with each organization having its own users, administrators, roles, and access policies. For example, a software company may provide a platform to hundreds of business customers. Each customer organization may need to manage its own employees while accessing only the resources associated with its organization.
-
This makes multi-tenancy and organization management central components of B2B IAM. A B2B IAM system may allow administrators to create organizations, invite users, define roles, configure SSO, manage permissions, and delegate identity administration to the customer organization.
-
B2B IAM also commonly requires multiple enterprise identity standards such as SAML and OpenID Connect (OIDC) SSO, Just-in-Time (JIT) provisioning.
-
There are also usual requirements for System for Cross-domain Identity Management (SCIM), role-based access control, delegated administration, and organization-level policies.
For example, when a business customer signs up for a SaaS application, its administrator may want employees to sign in using the company's existing identity provider rather than creating separate passwords. The customer's administrator may also need to control which employees can access the application and what those employees are allowed to do.
This makes B2B IAM more than simply "CIAM for businesses." The identity model needs to understand the relationship between users, organizations, roles, resources, and delegated administrators. The objective is to provide secure access while allowing organizations to maintain control over their own users.
IAM vs. CIAM: What's the True Difference?
IAM and CIAM are often described simply as "IAM is for employees, while CIAM is for customers." Although this is directionally correct, it does not capture the full difference between the two.
The more meaningful distinction is who owns the identity relationship, how the identity is managed, and what the organization is trying to achieve with that identity.
| Traditional IAM | CIAM | B2B IAM | |
|---|---|---|---|
| Primary identities | Employees, workforce users, contractors | Customers | Business customers, partners, suppliers, distributors, franchisees |
| Relationship with organization | Organization controls the identity | Customer chooses to interact with the organization | Organization-to-organization relationship |
| Typical use cases | Internal applications, corporate systems, employee access | Websites, mobile apps, SaaS products, e-commerce, consumer services | B2B SaaS, partner portals, supplier portals, customer portals |
| Key capabilities | SSO, MFA, RBAC, provisioning, de-provisioning, directory integration, PAM | Social login, passwordless, passkeys, MFA, progressive profiling, adaptive authentication, consent management | Multi-tenancy, organization management, SSO, SAML/OIDC, JIT, SCIM, delegated administration, RBAC |
| Primary focus | Security, governance, and administrative control | Security, customer experience, scalability, and conversion | Secure collaboration, organizational control, and delegated access |
In simple terms, traditional IAM is primarily designed to secure the workforce, CIAM is designed to secure and enable customer relationships, and B2B IAM is designed to secure relationships between organizations and their external business users.
All three are concerned with the same fundamental question: who is requesting access, and what should they be allowed to do? The difference lies in the identity relationship, the access environment, and the experience required to answer that question effectively.
Identity Management Best Practices
Here are the best practices to enable a smooth and seamless integration of a modern IAM program.
Define your IAM vision with a strong foundation
Your IAM should be a combination of modern technologies and business processes. You need to understand your current IT and network infrastructure and build your future capabilities around it.
Later, incorporate authorization, privileges, policies, and other constraints to ensure secure access into your web properties. Include a thorough assessment of the capabilities of the IAM product and its sync with organizational IT. An efficient risk evaluation should ideally cover:
-
An understanding of what third-party apps are currently in use.
-
What are your technological strengths and limitations?
Identity should be your core security perimeter
Organizations should move from the conventional focus of securing a network to securing identity. Centralize security controls around the identities of users and facilities rather than network-based perimeters.
Stage-wise implementation
An IAM program is usually implemented based on the two practices mentioned above. However, to avoid any complications, most IAM experts recommend a stage-wise implementation process.
Conduct a stakeholder awareness program
Your stakeholder awareness program should cover detailed training about your product abilities, scalability standards, and what technologies you are using. However, more than anyone, train your IT teams as they should most definitely know about your IAM's core capabilities.
Enable multi-factor authentication (MFA)
MFA is a crucial part of identity and access management. After all, it adds multiple security layers to user identities before allowing access to an application or database. Therefore, ensure that you have enabled MFA for all users and consumers, including IT admins and C-suite executives.
Implement Single Sign-On (SSO)
Establish SSO for all your web properties (devices, apps, and services) so consumers can use the same set of credentials to access multiple resources. This reduces login friction and password fatigue, but also eliminates issues related to weak password habits.
Enforce a zero-trust policy
Zero Trust is a holistic approach to network security where consumer identities are strictly verified, regardless of whether they are located inside or outside the network perimeter. However, it is only effective when you track and verify the access rights and privileges of consumers on an ongoing basis.
Implement a strong password policy
Enforce a strong password policy for both employees and your consumers. Make sure they are updating passwords regularly and aren't using sequential and repetitive characters.
Secure all privileged accounts
A good way to protect your critical business asset is to secure all privileged accounts. For starters, limit the number of users who have access to those accounts.
Conduct access audits from time to time
Regularly conduct access audits to ensure that whatever access you have granted is still required. You can offer additional access or revoke consumer access based on your audit report.
Favor passwordless login
Passwordless login simplifies and streamlines the authentication process by swapping traditional passwords with more secure factors. These extra-security methods may include a magic link, fingerprint, PIN, or a secret token delivered via email or text message.
Benefits of Identity and Access Management
Reduces security risk
Organizations can use identity and access management solutions to detect unauthorized access privileges, validations, or policy violations under a single system. You can also ensure that your organization meets necessary regulatory and audit requirements.
Easy to use
With IAM, it is easier to provision and manage access to end-users and system administrators. It also simplifies and secures the process of registration and authentication.
Reduces IT costs
Using IAM can lower operation costs to quite an extent. For example, with federated identity, organizations can integrate third-party services into their system. Similarly, with cloud IAM organizations need not buy or maintain on-premise infrastructure.
Improves user experience
SSO removes the need for users to recall and enter multiple passwords. Gone are the days of trying to remember dozens of password variations. With SSO, every time consumers switch to a new connected device, they can enjoy automatic logins.
Enhances security profiles
Modern IAM systems use SSO with additional levels of protection. A majority of these systems use Security Assertion Markup Language (SAML) 2.0 that can authenticate and authorize users based on the access level indicated in their directory profiles.
A few other benefits of identity and access management system include:
-
It enables secure, low-friction access through seamless authentication to different web properties.
-
It demonstrates an extreme degree of scalability by anticipating potential surges and dips in consumer registrations and activities.
-
It provides a unified experience by utilizing consolidated reports and analytics of user demographics, social registration and login data, revenue activities, and more.
-
It adheres to privacy regulations for protecting data in transit and at rest.
-
It keeps user data protected at all times by developing flexible schemas to get the most out of a system.
Modern IAM Trends
Modern IAM is increasingly focused on reducing dependence on passwords, continuously evaluating identity risk, enforcing least-privilege access, and detecting threats that target identities themselves. At the same time, organizations are looking for ways to provide stronger security without creating additional friction for employees, customers, and business users.
Here are some of the key trends shaping modern IAM:
Passwordless Authentication
Passwords have traditionally been one of the most common methods of authenticating users. However, passwords are also vulnerable to phishing, credential stuffing, brute-force attacks, password reuse, and other forms of credential theft. Managing passwords also creates friction for users, particularly when they need to remember and reset credentials across multiple applications.
Passwordless authentication addresses these challenges by allowing users to authenticate without entering a traditional password. Instead, the identity system can use methods such as passkeys, biometrics, security keys, magic links, or other cryptographic authentication mechanisms to verify the user's identity.
Passkeys are becoming an important part of this transition. They use public-key cryptography to authenticate users without requiring the organization to store a reusable password. A passkey can also use a device's biometric authentication, such as a fingerprint or facial recognition, to verify the user locally while keeping the underlying authentication credentials protected.
The goal of passwordless authentication is not simply to remove passwords. It is to create an authentication experience that is more resistant to credential-based attacks while also being easier for users. As organizations adopt passwordless authentication, IAM platforms increasingly need to support multiple authentication methods and choose the appropriate method based on the application, user, device, and level of risk.
Zero Trust Security
Zero Trust is a security approach based on the principle that no user, device, or application should automatically be trusted simply because it is inside an organization's network. Instead, access should be continuously evaluated based on identity, context, security policies, and the resource being requested.
Traditional security models often relied heavily on network boundaries. Once a user successfully entered the corporate network, they could potentially have access to a broad set of internal resources. Cloud computing, remote work, SaaS applications, and distributed infrastructure have made this model increasingly difficult to maintain.
Identity is therefore a central component of Zero Trust security. Before granting access, organizations can evaluate factors such as the user's identity, role, device, location, authentication method, requested resource, and current risk level. Access can then be granted, denied, or subjected to additional verification.
For example, a user may normally be allowed to access an application from a trusted device. If the same account suddenly attempts to access a sensitive resource from an unfamiliar device or unusual location, the organization may require additional authentication or block the request altogether.
Zero Trust does not mean asking users to authenticate repeatedly for every action. Instead, modern IAM systems use contextual and risk-based policies to determine when additional verification is actually necessary. This allows organizations to strengthen security while minimizing unnecessary authentication friction.
Identity Governance
Identity governance focuses on ensuring that users have the right access to the right resources for the right reasons and for the appropriate amount of time. While IAM systems can authenticate users and enforce access policies, identity governance provides the processes and controls needed to manage access throughout the identity lifecycle.
Organizations often have thousands of users accessing hundreds or even thousands of applications. Over time, employees can change roles, move between departments, receive additional permissions, or accumulate access that they no longer require. Without proper governance, this can result in excessive privileges and increase the organization's security and compliance risks.
Identity governance addresses these challenges through capabilities such as access reviews, entitlement management, role management, lifecycle management, segregation of duties, policy enforcement, and audit reporting. Organizations can use these controls to determine whether users still need the access they have been granted and whether that access complies with internal policies and regulatory requirements.
For example, an employee who moves from finance to another department may no longer need access to financial systems. Identity governance can help identify this outdated access and ensure that it is removed. Similarly, managers can periodically review the access rights of their teams and approve or revoke permissions as required.
As organizations adopt Zero Trust and least-privilege security models, identity governance becomes increasingly important. It provides the visibility and controls needed to ensure that access policies are not only defined but are also consistently maintained throughout the identity lifecycle.
Identity Threat Detection and Response (ITDR)
Identity Threat Detection and Response, or ITDR, is an emerging security discipline focused specifically on detecting and responding to threats that target identities, authentication systems, and access infrastructure.
Attackers increasingly target identities rather than attempting to directly compromise a network or application. Stolen credentials, compromised privileged accounts, session hijacking, MFA attacks, and malicious changes to identity configurations can allow attackers to gain legitimate-looking access to sensitive resources.
Traditional security tools may detect suspicious activity on endpoints, networks, or applications, but identity-based attacks can sometimes appear to be legitimate authentication or authorization events. ITDR addresses this gap by monitoring identity-related activity and looking for suspicious patterns.
For example, an ITDR system may detect an unusual sequence of events such as a privileged account logging in from an unfamiliar location, registering a new authentication method, changing access privileges, and subsequently accessing sensitive resources. Individually, these events may not always appear malicious, but their combination can indicate a compromised identity.
ITDR typically works alongside IAM, Security Information and Event Management (SIEM), Extended Detection and Response (XDR), and other security technologies. The objective is to provide security teams with greater visibility into identity-based threats and enable them to respond quickly by revoking sessions, disabling accounts, requiring additional authentication, or restricting access.
As identity becomes an increasingly important attack surface, ITDR is becoming an important extension of traditional IAM and cybersecurity practices.
AI-Powered Risk-Based Authentication
Risk-based authentication uses contextual information to determine how much authentication security a user should receive at a particular moment. Instead of treating every login attempt in exactly the same way, the system evaluates the risk associated with the request and adjusts the authentication requirements accordingly.
Traditional risk-based authentication can evaluate signals such as device information, IP address, geolocation, login history, failed authentication attempts, time of access, and user behavior. For example, a login from a familiar device and location may be considered low risk, while a login from a new device combined with an unusual location may trigger additional verification.
Artificial intelligence and machine learning can make this approach more sophisticated by analyzing large volumes of identity and behavioral signals and identifying patterns that may be difficult to detect using fixed rules alone. The system can establish a baseline of normal behavior and identify deviations that could indicate account compromise or suspicious activity.
For example, if a user normally accesses an application during business hours from a consistent device and suddenly attempts to access sensitive resources from a new device while exhibiting unusual behavior, an AI-powered risk engine can increase the risk score. The IAM system can then respond according to the organization's policy by allowing the request, requesting step-up authentication, limiting access, or blocking the transaction.
The key advantage is that security controls can become more dynamic. Rather than forcing every user through the highest level of authentication, organizations can apply stronger controls when the risk warrants them. This can improve security while maintaining a smoother experience for legitimate users.
AI-powered risk-based authentication is also becoming increasingly relevant as identity environments grow more complex. With employees, customers, partners, applications, APIs, and automated systems accessing resources across distributed environments, IAM systems need to evaluate more signals and make decisions in real time. AI can help organizations move from static authentication policies toward continuous, contextual, and adaptive identity security.
How IAM and Compliance Are Related to Each Other
Consumer data centricity is crucial to the success of any business today. Organizations should securely collect, manage, analyze, and protect their data. However, the method of capturing and safely storing user data can be difficult.
Many companies keep hundreds of separate data silos to get the job done. Fortunately, an identity and access management solution can help organizations break down these silos and store data into a unified database that provides a consistent view of the client across the business ecosystem.
Consumers want more control over their data at the same time. They want the nod on how brands use their data, they also wish to know precisely what they agreed to while using the product or service. An IAM solution offers trust and transparency to consumers by helping organizations ensure compliance with local and global regulations.
Speaking of regulations, many are industry-specific, such as the Health Insurance Portability and Accountability Act (HIPAA) for healthcare organizations. Others apply more broadly, such as the Payment Card Industry Data Security Standard (PCI DSS) that must be adopted by any organization that collects debit and credit card information.
The most disruptive regulations in recent years are the ones related to ensuring consumer privacy, such as the General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA).
| Security Program / Standard | What It Covers |
|---|---|
| OpenID | Open standards for authentication and identity verification that enable applications to verify a user's identity and obtain basic profile information. OpenID Connect builds on the OAuth 2.0 framework. |
| PCI DSS | A security standard designed to protect payment card data and secure organizations that store, process, or transmit payment card information. |
| ISO 27001 | An international standard for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). |
| ISO 27017 | Provides security controls and guidance specifically for the protection of information in cloud computing environments. |
| AICPA SOC 2 (Type II) | Evaluates an organization's controls against the AICPA Trust Services Criteria, including security, availability, processing integrity, confidentiality, and privacy, over a defined period of time. |
| ISAE 3000 | An international assurance standard for engagements covering non-financial information, including assessments of an organization's controls and compliance. |
| NIST Cybersecurity Framework (CSF) | A cybersecurity framework that helps organizations identify, assess, manage, and reduce cybersecurity risks through structured security practices. |
| CSA Cloud Controls Matrix (CCM) | A framework of cloud security controls developed by the Cloud Security Alliance to help organizations assess and improve the security of cloud environments. |
| CIS Critical Security Controls | A prioritized set of cybersecurity best practices designed to help organizations defend against common and evolving cyber threats. |
| EU-U.S. Privacy Shield | A former framework for regulating transfers of personal data between the European Union and the United States. It was invalidated by the Court of Justice of the European Union in 2020 and has since been replaced by the EU-U.S. Data Privacy Framework. |
| ISO/IEC 27018 | Provides guidance for protecting personally identifiable information (PII) in public cloud environments and establishes controls for cloud providers handling personal data. |
How LoginRadius CIAM Platform Can Accommodate Your Enterprise Requirements
With the right IAM provider, organizations can enjoy enormous time-saving, efficiency-building, and security-boosting benefits, irrespective of where they operate.
LoginRadius' extensive experience in the identity and access management market will help you build the right process for your enterprise.
LoginRadius offers you the following tools to help you build secure, seamless experiences for your consumers and B2B audiences.
-
Single Sign-On: LoginRadius SSO provides your users with a single identity to access all of your web assets, mobile applications, and third-party systems.
As your users navigate from one property to the next, you can recognize who they are, and document and access their activities in a central profile.
-
Multi-factor authentication: MFA verifies identities by adding additional layers of security to the authentication process. By requiring at least an extra step to verify identities, MFA ensures that the right consumer has the right access to your network.
It lifts off the burden of stolen or lost passwords on consumers and makes it harder for criminals to get into their accounts.
Additional forms of MFA by LoginRadius include security questions, biometric verification, automated phone calls, Google Authenticator, and social login.
-
Federated SSO: Federated SSO allows users to gain access to multiple organizations' web applications using one digital identity. LoginRadius supports standard SSO protocols like SAML, JWT, OAuth 2.0, OpenID Connect (OIDC), and Web Services Federation. The IAM platform offers a simple dashboard to manage all configurations required for these protocols.
-
User management: LoginRadius offers complete user management features, including:
-
Authorization: To validate the access rights of users.
-
Provisioning: To create user accounts.
-
Deprovisioning: To block, or delete user accounts.
-
Account Management: To disable user accounts, and grant, or restrict access.
-
Password Management: To trigger the password reset option for user accounts.
-
Compliance with privacy regulations: The LoginRadius Identity Platform handles consent management by ensuring continued compliance with all major privacy regulations, including the GDPR of the EU and the CCPA of California.
Conclusion
Powerful identity and access management solutions offer the right tools to ensure users can engage with enterprises at any time, from any device, securely. Organizations will need to rethink their business and operating models. There is a huge demand to invest in new digital methods of communication. And prioritizing digital security will go a long way.
FAQs
Q: What is the main purpose of IAM?
A: The main purpose of IAM is to ensure that the right identities (people or machines) have access to the right resources at the right time, for the right reasons, without compromising enterprise security.
Q: What is the difference between Authentication and Authorization?
A: Authentication verifies who you are (e.g., entering a password and an MFA code). Authorization determines what you are allowed to do once inside the system (e.g., viewing a document versus editing it).
Q: What is Single Sign-On (SSO)?
A: Single Sign-On is an authentication feature that allows a user to access multiple independent systems or applications using a single set of login credentials.
Q: Why is Zero Trust closely linked with IAM?
A: Zero Trust assumes that threats exist both outside and inside the network. Because Zero Trust relies on verifying every request explicitly, IAM serves as its foundation by validating user identity, device context, and access permissions continuously.